

Global Performance
6/6 locations ✓High global latency — average 2721ms across 6 locations, fastest from Madrid (2363ms), slowest from Santa Clara (3188ms). Assets on Cloudflare (host cdn-cookieyes.com, 6 assets); document served directly from origin (OVH). Cache-Control disables caching (no-store). 6 locations above the 500ms target.
Audit overview
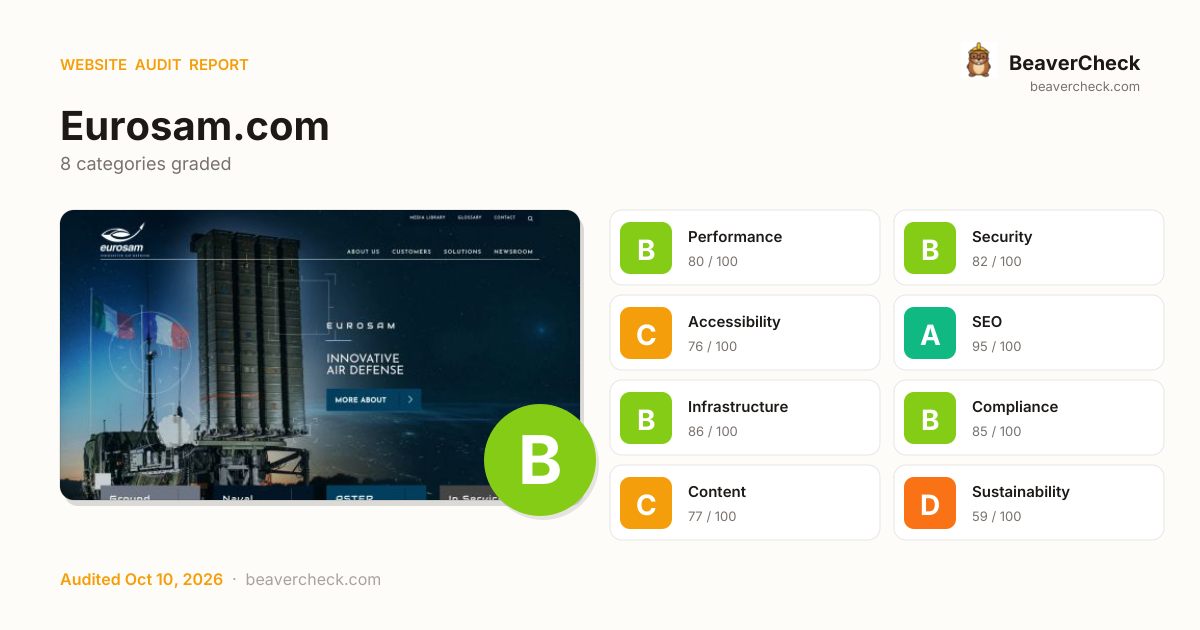
Sustainability needs attention; the rest of the categories are in good shape.
Fix Priority Matrix
5 findingsQuick Wins
2High impact, low effort — start here.
Strategic
3High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
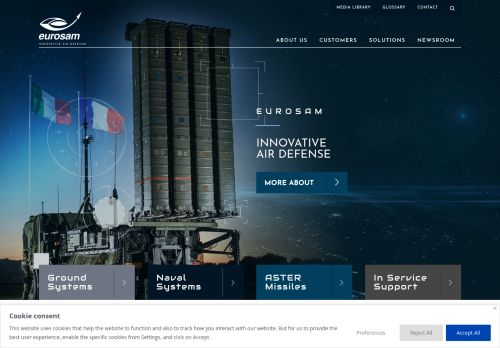
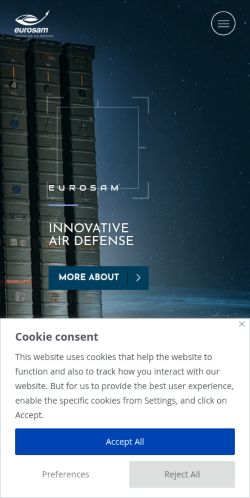
Screenshots
Your mail setup has problems.
eurosam.com fails 1 mail check: No DMARC record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
'unsafe-eval' found in script source
Unsafe value (unsafe-inline, unsafe-eval) in script-src defeats CSP's main protection — XSS injections can execute again.
'unsafe-inline' found in script source
Unsafe value (unsafe-inline, unsafe-eval) in script-src defeats CSP's main protection — XSS injections can execute again.
Cookie 'PHPSESSID' is missing the Secure flag
A cookie without the Secure flag can leak over HTTP — in HSTS-protected sites, this is still a defense-in-depth gap.
Page weighs 24.5 MB (19.6 MB transferred)
Informational: total page weight (uncompressed) and bytes actually transferred over the wire.
1 control(s) without accessible label
Form controls without labels — assistive tech announces 'edit text' with no context; users can't complete forms.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
€1,060 investment → €3,207/month returns + EUR 500,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
9 barrier(s) likely increasing bounce by ~38%.
- Page takes 20.6s to loadUsers abandon at ~3s — you're 18.1s over the 2.5s threshold→ Optimize render-blocking resources, preload the hero image, and compress images
- Page feels frozen for 643msClicks on the primary CTA are ignored while JavaScript runs→ Break up long tasks; defer non-critical JavaScript to post-hydration
- Mixed content on HTTPS pageBrowsers block insecure subresources — broken images, missing scripts, warning badge→ Change http:// URLs inside the page to https:// (or protocol-relative)
- Severe layout shift during page loadUsers mis-click when content jumps — converting intent into frustration→ Reserve space for images, ads, and embeds with explicit width/height
- 5 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
€500.000
- Skip navigation link is missing (WCAG 2.4.1)EAA: EUR 1.000 – EUR 500.000
- Multiple H1 headings (2 found)EAA: EUR 1.000 – EUR 500.000
- Heading level skipped: H3 → H5 (missing H4)EAA: EUR 1.000 – EUR 500.000
Bounce-Rate Cost
€3.202 /mo
+37.7pp bounce · ~3,767 lost visitors/mo
CPC: EUR 0.85
Bandwidth Waste
€4,57 /mo
61728.8 MB/mo × 0.074 EUR/GB
- Optimize transfer: save ~6.2 MB per page loadSaves €4,57/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 5 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
2.54 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
20.64 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
643 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.286
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
11.48 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
20.64 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
760 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
3.70 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
9 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.096
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
2.12 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
3.70 s
Categories
8Performance
Page weighs 24.5 MB (19.6 MB transferred)
Security
'unsafe-eval' found in script source
Accessibility
1 control(s) without accessible label
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of WordPress sites score 92+ on Sustainability; you're at 59 — closing this gap is the highest-leverage improvement.
Technology stack
WordPress, on Apache/PHP, hosted on Apache HTTP Server
Stack Architecture
 Google Analytics
 Google Tag Manager
 WooCommerce
 WordPress
 Bootstrap 4.6.0
 Google Font API HSTS
 LazySizes
 MediaElement.js 4.2.17
 Open Graph
 Popper
 Priority Hints
 RSS
 core-js 3.36.1
 jQuery 3.7.1 jQuery Migrate 3.4.1
 PHP 8.4
 Apache Apache HTTP Server
All Detected Technologies (19)
Apache is a free and open-source cross-platform web server software.
PHP is a general-purpose scripting language used for web development.
Bootstrap is a free and open-source CSS framework directed at responsive, mobile-first front-end web development. It contains CSS and JavaScript-based design templates for typography, forms, buttons, navigation, and other interface components.
Google Font API is a web service that supports open-source font files that can be used on your web designs.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
LazySizes is a JavaScript library used to delay the loading of images (iframes, scripts, etc) until they come into view.
MediaElement.js is a set of custom Flash plugins that mimic the HTML5 MediaElement API for browsers that don't support HTML5 or don't support the media codecs.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Popper is a positioning engine, its purpose is to calculate the position of an element to make it possible to position it near a given reference element.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
RSS is a family of web feed formats used to publish frequently updated works—such as blog entries, news headlines, audio, and video—in a standardized format.
core-js is a modular standard library for JavaScript, with polyfills for cutting-edge ECMAScript features.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
Query Migrate is a javascript library that allows you to preserve the compatibility of your jQuery code developed for versions of jQuery older than 1.9.
Google Analytics is a free web analytics service that tracks and reports website traffic.
Google Tag Manager is a tag management system (TMS) that allows you to quickly and easily update measurement codes and related code fragments collectively known as tags on your website or mobile app.
Observations (5)
Runtime exposed via X-Powered-By header
The X-Powered-By header reveals 'PHP 8.4'. Remove this header in production to reduce information leakage.
WordPress detected — review security configuration
WordPress sites benefit from: protecting wp-login.php, disabling XML-RPC if unused, restricting REST API access, and keeping all plugins and themes up to date. Check the Security tab for specific findings.
No build tool detected
A framework (Bootstrap) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Bootstrap version may be outdated
Detected Bootstrap 4.6.0. The current major version is 5. Consider updating for security patches and new features.
Complex technology stack detected
19 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/eurosam.com)<a href="https://beavercheck.com/sites/eurosam.com"><img src="https://beavercheck.com/badge?url=https%3A%2F%2FEurosam.com" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2FEurosam.comExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
3 sprints · 13h total → projected A (90)
Sprint 1: Quick Wins
+5Highest ROI — low effort, high impact
- · Page weighs 24.5 MB (19.6 MB transferred)
- · Cookie 'PHPSESSID' is missing the Secure flag
Sprint 2: Core Fixes
+1Medium effort, high structural impact
- · 1 control(s) without accessible label
Sprint 3: Strategic Improvements
+2Higher effort, long-term payoff
- · 'unsafe-eval' found in script source
- · 'unsafe-inline' found in script source