

Global Performance
6/6 locations ✓High global latency — average 613ms across 6 locations, fastest from Amsterdam (129ms), slowest from Santa Clara (980ms). No CDN (document or assets). Cache-Control header is missing. 4 locations above the 500ms target.
Audit overview
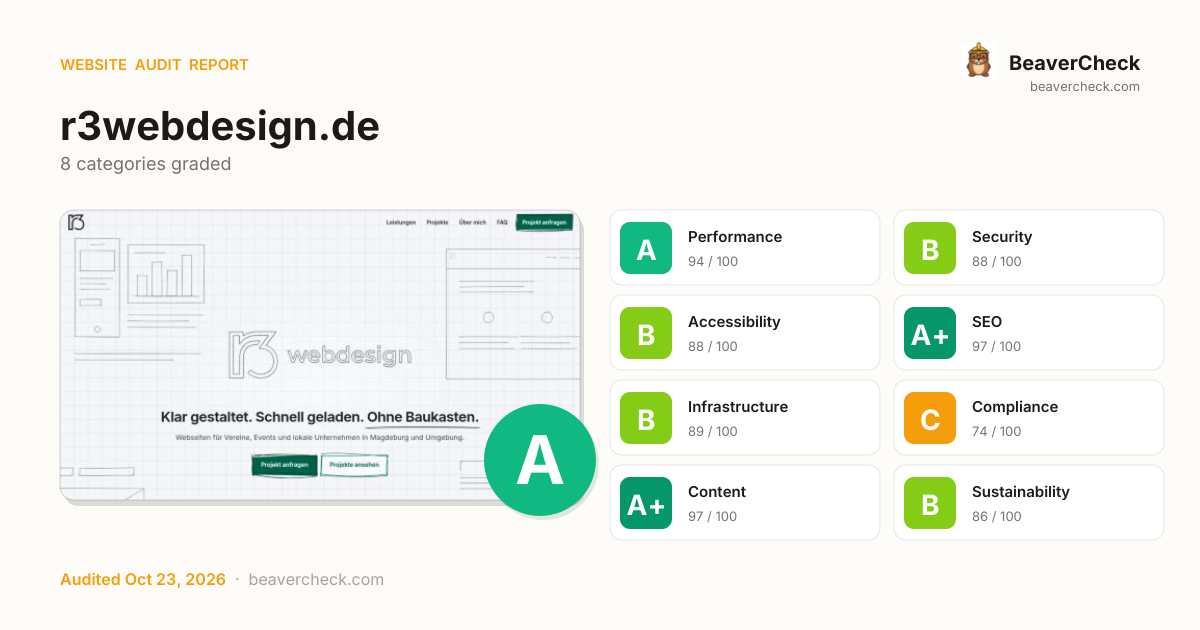
All categories sit comfortably above the 70 threshold; this is a clean audit.
Fix Priority Matrix
5 findingsQuick Wins
3High impact, low effort — start here.
Strategic
2High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
Screenshots
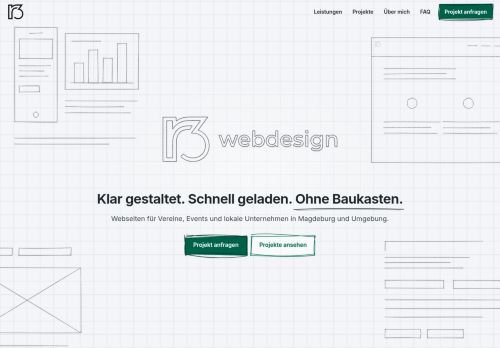
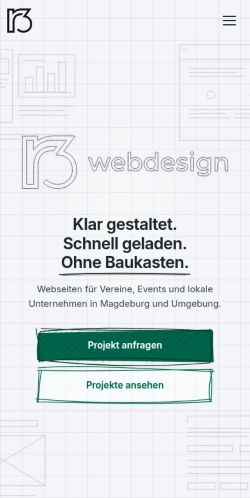
Your mail setup has problems.
r3webdesign.de fails 1 mail check: Subdomain policy (sp=none) is weaker than domain policy (p=reject). This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
Cross-Origin-Embedder-Policy header is missing
COEP enforces that all embedded resources opt-in to cross-origin embedding — required for cross-origin isolation features.
Cross-Origin-Opener-Policy header is missing
COOP isolates your top-level browsing context from cross-origin windows — without it, popup-based side-channel attacks remain possible.
HSTS is enabled but missing includeSubDomains
Without includeSubDomains, a forgotten dev subdomain over HTTP can set malicious cookies that ride to the apex.
No Permissions-Policy header
Permissions-Policy locks down browser APIs you don't use, shrinking the attack surface.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
€428 investment → €709/month returns + EUR 500,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
2 barrier(s) likely increasing bounce by ~3%.
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
- No skip-to-content linkKeyboard and screen-reader users must tab through the entire header on every page→ Add a visible-on-focus <a href="#main">Skip to content</a> as the first focusable element
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
€500.000
- Skip navigation link is missing (WCAG 2.4.1)EAA: EUR 1.000 – EUR 500.000
Bounce-Rate Cost
€709 /mo
+3.2pp bounce · ~322 lost visitors/mo
CPC: EUR 2.20
Bandwidth Waste
€0,03 /mo
420.7 MB/mo × 0.074 EUR/GB
- Optimize transfer: save ~42 KB per page loadSaves €0,03/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 1 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
1.58 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.70 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
34 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.005
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
3.00 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
1.72 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
554 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
600 ms
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.022
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.14 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
600 ms
Categories
8Performance
All checks pass
Security
Content-Security-Policy header is missing
Accessibility
All checks pass
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of Google Search Console sites score 86+ on Compliance; you're at 74 — closing this gap is the highest-leverage improvement.
Technology stack
Astro
Stack Architecture
 Astro Google Search Console HSTS
 HTTP/3
 Open Graph
 Priority Hints
All Detected Technologies (6)
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
Observations (1)
No build tool detected
A framework (Astro) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/r3webdesign.de)<a href="https://beavercheck.com/sites/r3webdesign.de"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fr3webdesign.de" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fr3webdesign.deExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 5h total → projected A (93)
Sprint 1: Quick Wins
+2Highest ROI — low effort, high impact
- · Cross-Origin-Opener-Policy header is missing
- · HSTS is enabled but missing includeSubDomains
- · No Permissions-Policy header
Sprint 2: Core Fixes
+1Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · Cross-Origin-Embedder-Policy header is missing