

Global Performance
6/6 locations ✓High global latency — average 1171ms across 6 locations, fastest from Amsterdam (415ms), slowest from Sao Paulo (2046ms). No CDN (document or assets). Cache-Control header is missing. 4 locations above the 500ms target.
Audit overview
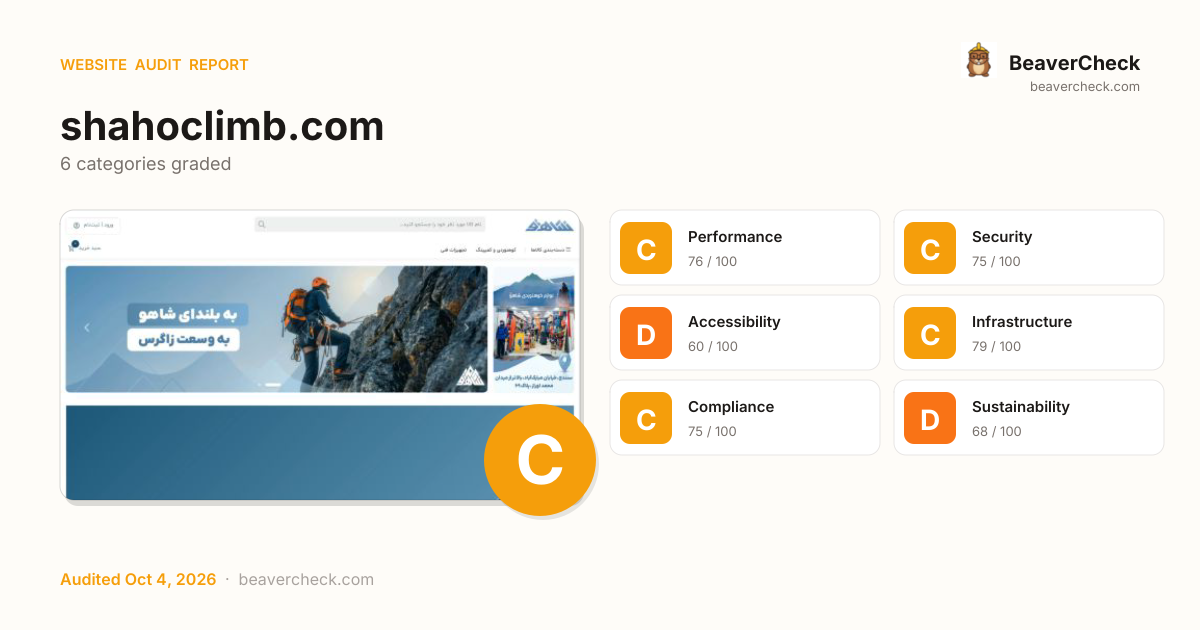
Accessibility and Sustainability need attention; the other categories are in good shape.
Fix Priority Matrix
5 findingsQuick Wins
3High impact, low effort — start here.
Strategic
2High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
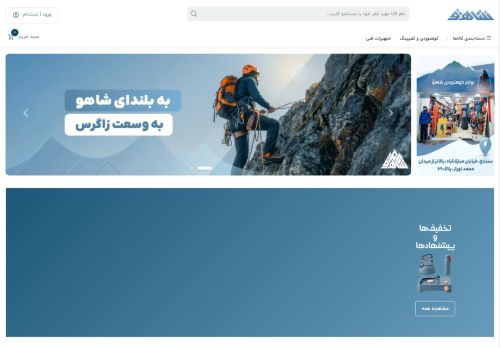
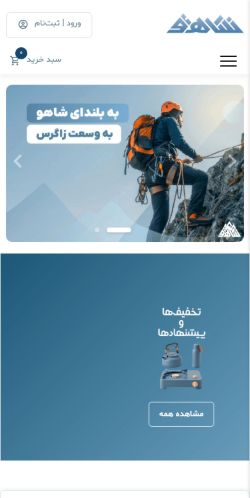
Screenshots
Your mail setup has problems.
shahoclimb.com fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
Page weighs 4.4 MB (4.5 MB transferred)
Informational: total page weight (uncompressed) and bytes actually transferred over the wire.
Cross-Origin-Embedder-Policy header is missing
COEP enforces that all embedded resources opt-in to cross-origin embedding — required for cross-origin isolation features.
Cross-Origin-Opener-Policy header is missing
COOP isolates your top-level browsing context from cross-origin windows — without it, popup-based side-channel attacks remain possible.
HSTS is enabled but max-age is short (2592000s, should be >= 31536000s)
HSTS is on, but a short max-age means browsers forget the policy sooner than recommended — set >= 1 year.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
IRR 6,500,000 investment → IRR 383,226,145/month returns
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
5 barrier(s) likely increasing bounce by ~34%.
- Page takes 14.8s to loadUsers abandon at ~3s — you're 12.3s over the 2.5s threshold→ Optimize render-blocking resources, preload the hero image, and compress images
- Severe layout shift during page loadUsers mis-click when content jumps — converting intent into frustration→ Reserve space for images, ads, and embeds with explicit width/height
- No viewport meta tagMobile browsers render at desktop width and shrink — text unreadable, tap targets miniature→ Add <meta name="viewport" content="width=device-width, initial-scale=1">
- HSTS is enabled but max-age is short (2592000s)First-visit protection is in place, but browsers forget the policy sooner than recommended→ Raise Strict-Transport-Security max-age to at least 31536000 (1 year)
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Bounce-Rate Cost
IRR 383,179,044 /mo
+33.9pp bounce · ~3,390 lost visitors/mo
CPC: IRR 113025.21
Bandwidth Waste
IRR 47,101 /mo
14012.5 MB/mo × 3361.345 IRR/GB
- Optimize transfer: save ~1.4 MB per page loadSaves IRR 47,101/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 2 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
10.11 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
14.76 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
60 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
1.491
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
10.11 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
18.10 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
2.08 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
4.96 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.763
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
3.23 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
4.99 s
Categories
6How you compare
Where this site stands against peers running the same stack.
Top 10% of HSTS sites score 95+ on Infrastructure; you're at 79 — closing this gap is the highest-leverage improvement.
Technology stack
HSTS, on IIS/ASP.NET, hosted on Microsoft IIS
Stack Architecture
 Microsoft ASP.NET
 Windows Server ASP.NET
 IIS 10.0 Microsoft IIS 10.0
All Detected Technologies (6)
Internet Information Services (IIS) is an extensible web server software created by Microsoft for use with the Windows NT family.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
ASP.NET is an open-source, server-side web-application framework designed for web development to produce dynamic web pages.
Windows Server is a brand name for a group of server operating systems.
Observations (2)
Server version exposed in headers
The Server header reveals 'IIS 10.0'. Exposing exact server versions helps attackers target known vulnerabilities. Consider configuring your server to hide version information.
No build tool detected
A framework (HSTS) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/shahoclimb.com)<a href="https://beavercheck.com/sites/shahoclimb.com"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fshahoclimb.com" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fshahoclimb.comExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 4h total → projected B (81)
Sprint 1: Quick Wins
+5Highest ROI — low effort, high impact
- · Page weighs 4.4 MB (4.5 MB transferred)
- · HSTS is enabled but max-age is short (2592000s, should be >= 31536000s)
- · Cross-Origin-Opener-Policy header is missing
Sprint 2: Core Fixes
+3Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · Cross-Origin-Embedder-Policy header is missing