

Global Performance
6/6 locations ✓High global latency — average 1350ms across 6 locations, fastest from Madrid (936ms), slowest from Sao Paulo (2030ms). Assets on Cloudflare (host cdnjs.cloudflare.com, 4 assets); document served directly from origin. Cache-Control header is missing. 6 locations above the 500ms target.
Audit overview
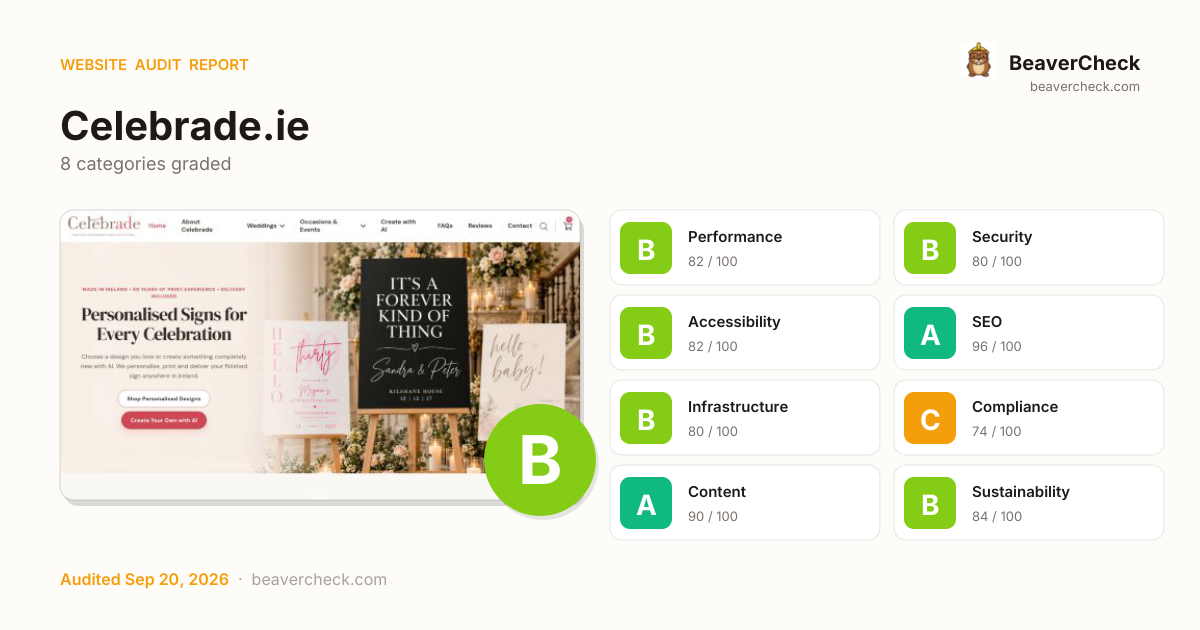
All categories sit comfortably above the 70 threshold; this is a clean audit.
Fix Priority Matrix
5 findingsQuick Wins
4High impact, low effort — start here.
Strategic
1High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
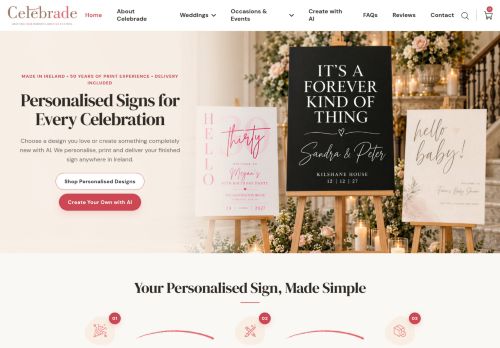
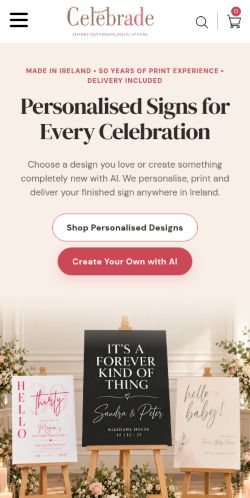
Screenshots
Your mail setup has problems.
celebrade.ie fails 1 mail check: DMARC policy is none — monitoring only. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
HSTS header is missing
Without HSTS, a network attacker can downgrade the very first connection to HTTP and steal the user's session.
Soft 404: server returns HTTP 200 for non-existent pages
Soft 404s (HTTP 200 for missing pages) confuse Google — it indexes the 'not found' page as real content and ranks it.
1 software version(s) disclosed in HTML: Site Kit by Google 1.187.0
Each disclosed version enables direct CVE lookup -- attacker reads the version, searches the CVE database, targets the site with a tested exploit.
16 render-blocking stylesheet(s) -- recommended: <=3
Informational: a Permissions-Policy directive showing feature -> allowed origins.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
€340 investment → €5,601/month returns
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
6 barrier(s) likely increasing bounce by ~27%.
- Page takes 4.7s to loadUsers abandon at ~3s — you're 2.2s over the 2.5s threshold→ Optimize render-blocking resources, preload the hero image, and compress images
- 3 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
- High main-thread blocking timePage is non-interactive for 397ms after first paint→ Defer third-party scripts and split large bundles
- No HSTS headerReturning visitors are briefly exposed to downgrade attacks on first request→ Set Strict-Transport-Security: max-age=31536000; includeSubDomains
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Bounce-Rate Cost
€2.876 /mo
+26.8pp bounce · ~2,677 lost visitors/mo
CPC: EUR 1.07
Bandwidth Waste
€0,34 /mo
4528.9 MB/mo × 0.074 EUR/GB
- Optimize transfer: save ~453 KB per page loadSaves €0,34/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 3 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
4.11 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
4.66 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
397 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.018
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
27.23 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
9.20 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
2.13 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
2.42 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
4 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.060
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
2.43 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
2.48 s
Categories
8Performance
16 render-blocking stylesheet(s) -- recommended: <=3
Security
Content-Security-Policy header is missing
Accessibility
Soft 404: server returns HTTP 200 for non-existent pages
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of Cart Functionality sites score 93+ on Infrastructure; you're at 80 — closing this gap is the highest-leverage improvement.
Technology stack
WordPress, on PHP, with Cloudflare CDN
Stack Architecture
 Google Analytics
 Google Tag Manager
 Cart Functionality
 WooCommerce
 WordPress
 Bootstrap 5.3.8
 Font Awesome 7.0.1
 Google Font API
 OWL Carousel
 Open Graph
 Priority Hints Twitter Emoji (Twemoji)
 jQuery 3.7.1 jQuery Migrate 3.4.1
 PHP 8.4.24
 Cloudflare
 Nginx
 cdnjs
All Detected Technologies (18)
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
Nginx is a web server that can also be used as a reverse proxy, load balancer, mail proxy and HTTP cache.
cdnjs is a free distributed JS library delivery service.
PHP is a general-purpose scripting language used for web development.
Websites that have a shopping cart or checkout page, either using a known ecommerce platform or a custom solution.
Bootstrap is a free and open-source CSS framework directed at responsive, mobile-first front-end web development. It contains CSS and JavaScript-based design templates for typography, forms, buttons, navigation, and other interface components.
Font Awesome is a font and icon toolkit based on CSS and Less.
Google Font API is a web service that supports open-source font files that can be used on your web designs.
OWL Carousel is an enabled jQuery plugin that lets you create responsive carousel sliders.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
Twitter Emoji is a set of open-source emoticons and emojis for Twitter, TweetDeck, and also for Android and iOS versions of the application.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
Query Migrate is a javascript library that allows you to preserve the compatibility of your jQuery code developed for versions of jQuery older than 1.9.
Google Analytics is a free web analytics service that tracks and reports website traffic.
Google Tag Manager is a tag management system (TMS) that allows you to quickly and easily update measurement codes and related code fragments collectively known as tags on your website or mobile app.
Observations (4)
Runtime exposed via X-Powered-By header
The X-Powered-By header reveals 'PHP 8.4.24'. Remove this header in production to reduce information leakage.
WordPress detected — review security configuration
WordPress sites benefit from: protecting wp-login.php, disabling XML-RPC if unused, restricting REST API access, and keeping all plugins and themes up to date. Check the Security tab for specific findings.
No build tool detected
A framework (Bootstrap) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
18 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/celebrade.ie)<a href="https://beavercheck.com/sites/celebrade.ie"><img src="https://beavercheck.com/badge?url=https%3A%2F%2FCelebrade.ie" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2FCelebrade.ieExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 4h total → projected A (90)
Sprint 1: Quick Wins
+6Highest ROI — low effort, high impact
- · HSTS header is missing
- · Soft 404: server returns HTTP 200 for non-existent pages
- · 16 render-blocking stylesheet(s) -- recommended: <=3
- · 1 software version(s) disclosed in HTML: Site Kit by Google 1.187.0
Sprint 2: Core Fixes
+1Medium effort, high structural impact
- · Content-Security-Policy header is missing