

Global Performance
6/6 locations ✓High global latency — average 540ms across 6 locations, fastest from Santa Clara (409ms), slowest from Sao Paulo (793ms). Document on Shopify; assets also on Cloudflare. Cache-Control header is missing. 4 locations above the 500ms target.
Audit overview
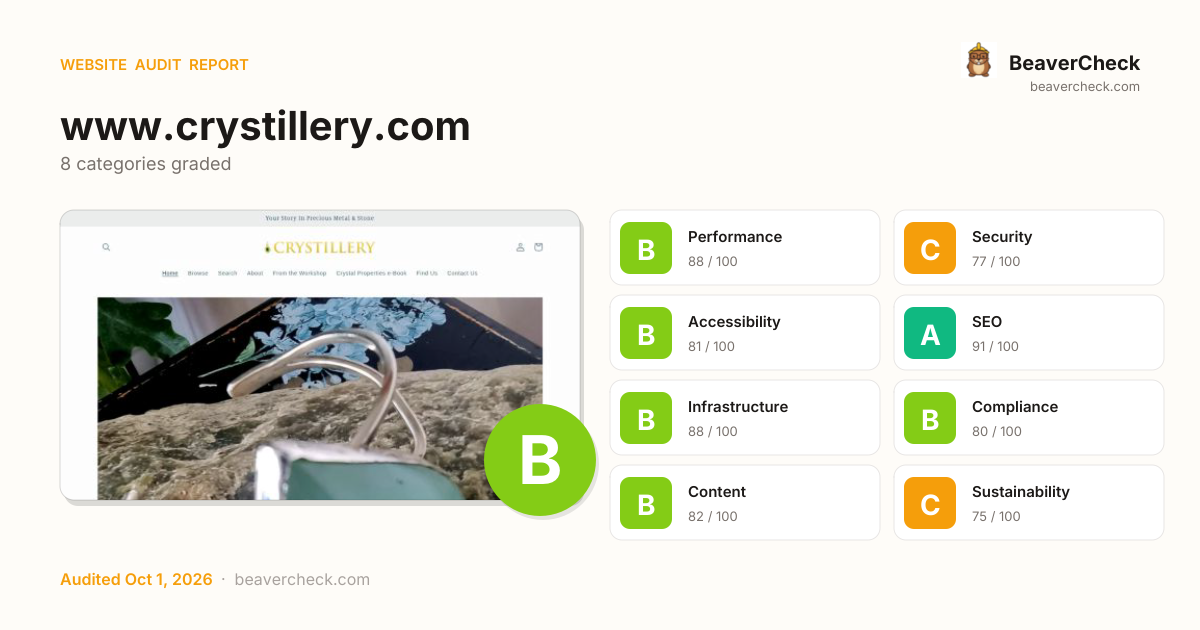
All categories sit comfortably above the 70 threshold; this is a clean audit.
Fix Priority Matrix
5 findingsQuick Wins
3High impact, low effort — start here.
Strategic
2High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
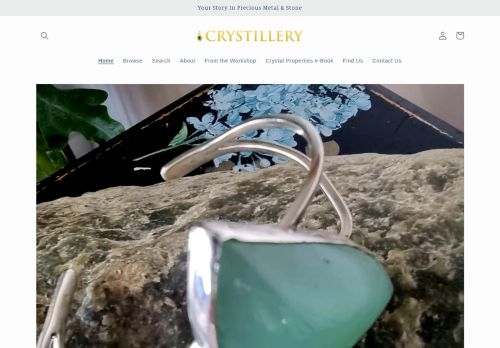
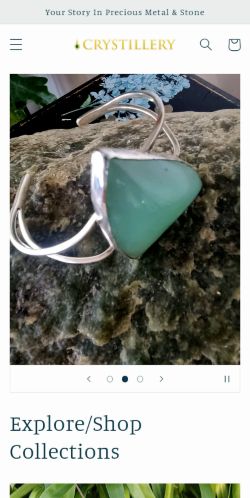
Screenshots
Your mail setup has problems.
crystillery.com fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
HSTS header is missing
Without HSTS, a network attacker can downgrade the very first connection to HTTP and steal the user's session.
1 link(s) with no accessible text
Links with no accessible text (empty <a></a>, image-only no alt, icon-only no aria-label) are unidentifiable to screen readers.
1 link(s) open in a new tab without rel=noopener
target="_blank" without rel="noopener" lets the destination tab navigate the original via window.opener -- a reverse-tabnabbing phishing primitive.
225 HTTP requests — consider bundling or reducing
High HTTP request count — bundling, sprite-ing, and HTTP/2 server push can reduce per-request overhead.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
€680 investment → €7,737/month returns + EUR 500,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
5 barrier(s) likely increasing bounce by ~25%.
- Page takes 8.6s to loadUsers abandon at ~3s — you're 6.1s over the 2.5s threshold→ Optimize render-blocking resources, preload the hero image, and compress images
- 12 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
- High main-thread blocking timePage is non-interactive for 246ms after first paint→ Defer third-party scripts and split large bundles
- No HSTS headerReturning visitors are briefly exposed to downgrade attacks on first request→ Set Strict-Transport-Security: max-age=31536000; includeSubDomains
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
€500.000
- 2 of 2 <nav> elements are unlabeledEAA: EUR 1.000 – EUR 500.000
- 1 empty heading(s)EAA: EUR 1.000 – EUR 500.000
Bounce-Rate Cost
€2.704 /mo
+25.2pp bounce · ~2,517 lost visitors/mo
CPC: EUR 1.07
Bandwidth Waste
€0,58 /mo
7795.5 MB/mo × 0.074 EUR/GB
- Optimize transfer: save ~780 KB per page loadSaves €0,58/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 3 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
3.51 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
8.60 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
246 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
6.05 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
8.87 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
574 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.34 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.32 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
1.37 s
Categories
8Performance
225 HTTP requests — consider bundling or reducing
Security
Content-Security-Policy header is missing
Accessibility
1 link(s) with no accessible text
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of Cart Functionality sites score 96+ on SEO; you're at 91 — closing this gap is the highest-leverage improvement.
Technology stack
HTTP/3, with Cloudflare CDN
Stack Architecture
 American Express
 Apple Pay
 Google Pay
 Mastercard
 PayPal
 Shop Pay
 Visa
 Cart Functionality
 Shopify
 HTTP/3
 Open Graph
 Priority Hints
 core-js 2.6.12
 Cloudflare
All Detected Technologies (14)
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
Websites that have a shopping cart or checkout page, either using a known ecommerce platform or a custom solution.
Shopify is a subscription-based software that allows anyone to set up an online store and sell their products. Shopify store owners can also sell in physical locations using Shopify POS, a point-of-sale app and accompanying hardware.
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
core-js is a modular standard library for JavaScript, with polyfills for cutting-edge ECMAScript features.
American Express, also known as Amex, facilitates electronic funds transfers throughout the world, most commonly through branded credit cards, debit cards and prepaid cards.
Apple Pay is a mobile payment and digital wallet service by Apple that allows users to make payments in person, in iOS apps, and on the web.
Google Pay is a digital wallet platform and online payment system developed by Google to power in-app and tap-to-pay purchases on mobile devices, enabling users to make payments with Android phones, tablets or watches.
MasterCard facilitates electronic funds transfers throughout the world, most commonly through branded credit cards, debit cards and prepaid cards.
PayPal is an online payments system that supports online money transfers and serves as an electronic alternative to traditional paper methods like checks and money orders.
Shop Pay is an accelerated checkout that lets customers save their email address, credit card, and shipping and billing information so they can complete their transaction faster the next time they are directed to the Shopify checkout.
Observations (3)
Shopify storefront detected
Shopify handles hosting, SSL, and CDN automatically. Performance optimizations focus on theme code, app scripts, and image optimization. Check the Performance tab for third-party script impact.
No build tool detected
A framework (HTTP/3) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
14 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/crystillery.com)<a href="https://beavercheck.com/sites/crystillery.com"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fwww.crystillery.com" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fwww.crystillery.comExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 8h total → projected A (91)
Sprint 1: Quick Wins
+5Highest ROI — low effort, high impact
- · HSTS header is missing
- · 1 link(s) with no accessible text
- · 1 link(s) open in a new tab without rel=noopener
Sprint 2: Core Fixes
+3Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · 225 HTTP requests — consider bundling or reducing