

Global Performance
6/6 locations ✓High global latency — average 1010ms across 6 locations, fastest from Madrid (713ms), slowest from Santa Clara (1329ms). Cloudflare edge cache (DYNAMIC). Cache-Control disables caching (no-store). 6 locations above the 500ms target.
Audit overview
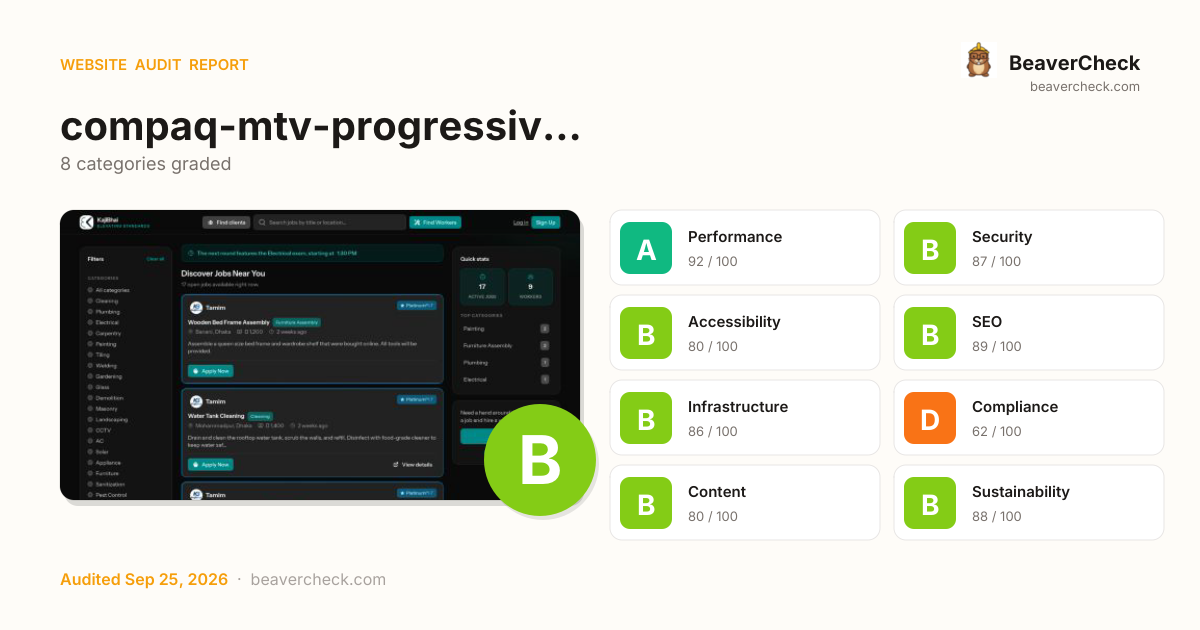
Compliance needs attention; the rest of the categories are in good shape.
Fix Priority Matrix
5 findingsQuick Wins
3High impact, low effort — start here.
Strategic
2High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
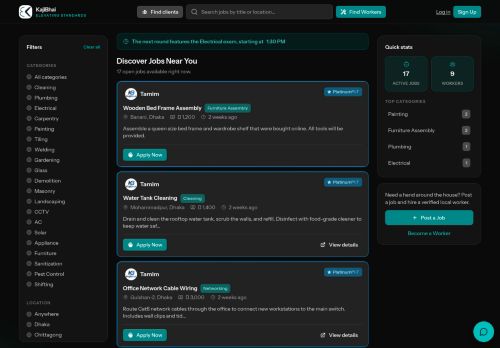
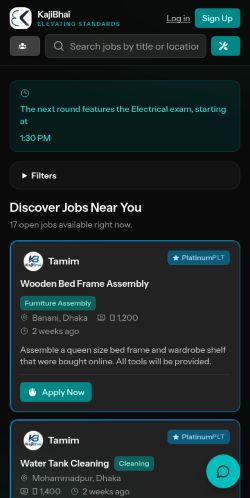
Screenshots
Your mail setup has problems.
compaq-mtv-progressive-surgeons.trycloudflare.com fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
'unsafe-eval' found in script source
Unsafe value (unsafe-inline, unsafe-eval) in script-src defeats CSP's main protection — XSS injections can execute again.
No DMARC record found
Without DMARC, anyone can send phishing emails using your domain name.
No Permissions-Policy header
Permissions-Policy locks down browser APIs you don't use, shrinking the attack surface.
No SPF record found
Security gaps expose your site and users to attacks, eroding trust.
Permissions-Policy header is missing
Permissions-Policy locks down browser APIs you don't use — without it, every page can request camera/mic/geolocation if XSS lands.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
$800 investment → $1,280/month returns + USD 157,500 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
2 barrier(s) likely increasing bounce by ~5%.
- No structured dataNo rich-result eligibility in Google — lower SERP CTR vs competitors with stars and prices→ Add JSON-LD for your page type (Product, Article, FAQPage, LocalBusiness, …)
- No skip-to-content linkKeyboard and screen-reader users must tab through the entire header on every page→ Add a visible-on-focus <a href="#main">Skip to content</a> as the first focusable element
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
$157,500
- No privacy policy found (page links and common paths checked)CCPA/CPRA: USD 2,500 – USD 7,500
- Privacy Policy not detectedCCPA/CPRA: USD 2,500 – USD 7,500
- No <nav> landmark foundADA Title III: USD 25,000 – USD 150,000
Bounce-Rate Cost
$1,280 /mo
+4.8pp bounce · ~476 lost visitors/mo
CPC: USD 2.69
Bandwidth Waste
$0.08 /mo
975.3 MB/mo × 0.080 USD/GB
- Optimize transfer: save ~98 KB per page loadSaves $0.08/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 1 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
1.45 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.45 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
58 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.061
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
2.30 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
2.87 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
684 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
684 ms
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
12 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.005
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.28 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
980 ms
Categories
8Performance
All checks pass
Security
'unsafe-eval' found in script source
Accessibility
All checks pass
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of HSTS sites score 86+ on Compliance; you're at 62 — closing this gap is the highest-leverage improvement.
Technology stack
Alpine.js 3.15.12, on PHP, with Cloudflare CDN
Stack Architecture
 Alpine.js 3.15.12HSTS
 Laravel
 Livewire
 Open Graph
 Tailwind CSS
 PHP 8.2.34
 Cloudflare
All Detected Technologies (8)
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
PHP is a general-purpose scripting language used for web development.
Alpine.js is a minimal framework for composing behavior directly in your markup.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
Laravel is a free, open-source PHP web framework.
Livewire is a full-stack Laravel framework for building dynamic interfaces.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Observations (3)
Runtime exposed via X-Powered-By header
The X-Powered-By header reveals 'PHP 8.2.34'. Remove this header in production to reduce information leakage.
No build tool detected
A framework (Alpine.js) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
8 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/compaq-mtv-progressive-surgeons.trycloudflare.com)<a href="https://beavercheck.com/sites/compaq-mtv-progressive-surgeons.trycloudflare.com"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fcompaq-mtv-progressive-surgeons.trycloudflare.com" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fcompaq-mtv-progressive-surgeons.trycloudflare.comExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
3 sprints · 8h total → projected B (88)
Sprint 1: Quick Wins
+2Highest ROI — low effort, high impact
- · No Permissions-Policy header
- · Permissions-Policy header is missing
- · No SPF record found
Sprint 2: Core Fixes
+1Medium effort, high structural impact
- · No DMARC record found
Sprint 3: Strategic Improvements
Higher effort, long-term payoff
- · 'unsafe-eval' found in script source