

Global Performance
6/6 locations ✓High global latency — average 1593ms across 6 locations, fastest from Amsterdam (213ms), slowest from Santa Clara (2372ms). No CDN (document or assets). Cache-Control header is missing. 4 locations above the 500ms target.
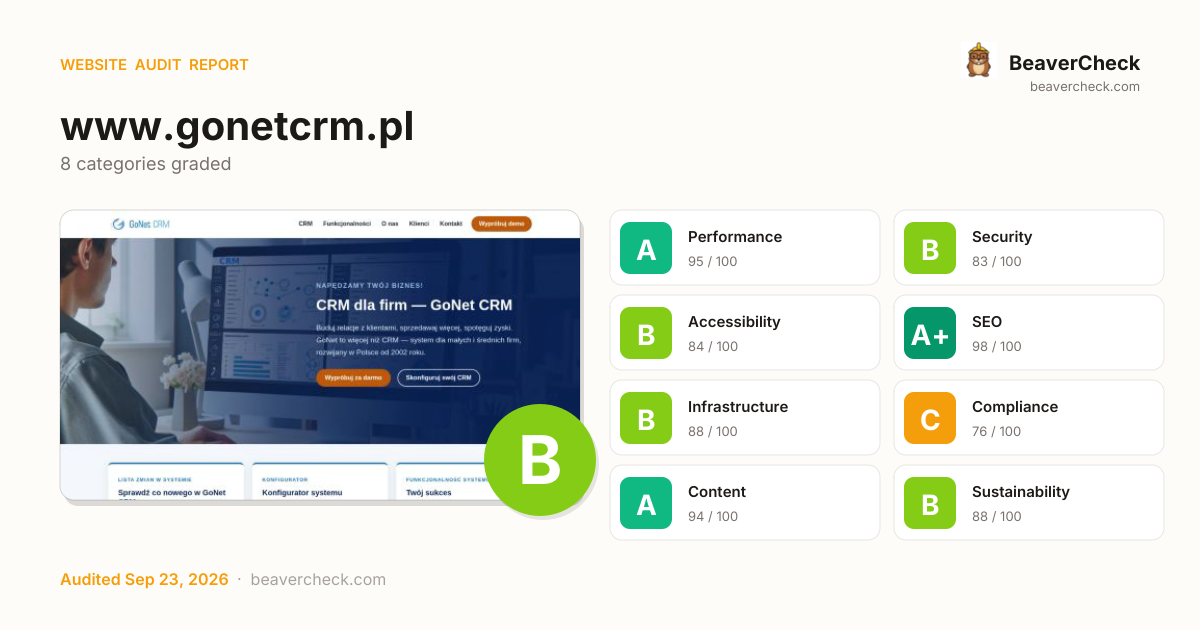
Audit overview
All categories sit comfortably above the 70 threshold; this is a clean audit.
Fix Priority Matrix
5 findingsQuick Wins
2High impact, low effort — start here.
Strategic
3High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
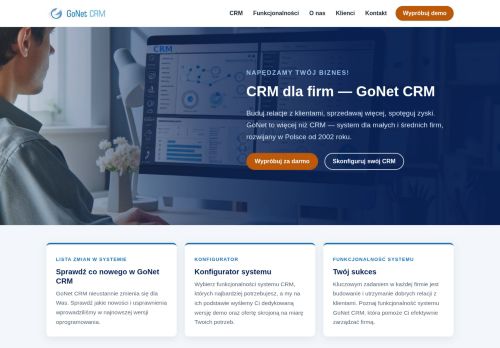
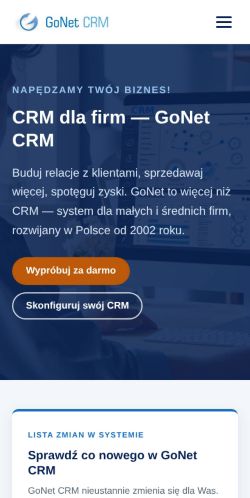
Screenshots
Your mail setup has problems.
gonetcrm.pl fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
HSTS header is missing
Without HSTS, a network attacker can downgrade the very first connection to HTTP and steal the user's session.
Cross-Origin-Embedder-Policy header is missing
COEP enforces that all embedded resources opt-in to cross-origin embedding — required for cross-origin isolation features.
Cross-Origin-Opener-Policy header is missing
COOP isolates your top-level browsing context from cross-origin windows — without it, popup-based side-channel attacks remain possible.
No DMARC record found
Without DMARC, anyone can send phishing emails using your domain name.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
PLN 825 investment → PLN 13,949/month returns + EUR 500,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
5 barrier(s) likely increasing bounce by ~10%.
- No HSTS headerReturning visitors are briefly exposed to downgrade attacks on first request→ Set Strict-Transport-Security: max-age=31536000; includeSubDomains
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
- Content is hard to readGraduate-level reading difficulty — limits the addressable audience for product or blog pages→ Shorten sentences; replace jargon with plain language; target Flesch ease ≥60
- No skip-to-content linkKeyboard and screen-reader users must tab through the entire header on every page→ Add a visible-on-focus <a href="#main">Skip to content</a> as the first focusable element
- 1 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
€500.000
- Skip navigation link is missing (WCAG 2.4.1)EAA: EUR 1.000 – EUR 500.000
Bounce-Rate Cost
PLN 13 948 /mo
+10.0pp bounce · ~996 lost visitors/mo
CPC: PLN 14.00
Bandwidth Waste
PLN 0,16 /mo
498.0 MB/mo × 0.320 PLN/GB
- Optimize transfer: save ~50 KB per page loadSaves PLN 0,16/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 2 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
908 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.96 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.03 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
1.98 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
247 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
450 ms
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
404 ms
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
454 ms
Categories
8Performance
All checks pass
Security
Content-Security-Policy header is missing
Accessibility
All checks pass
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of Open Graph sites score 87+ on Compliance; you're at 76 — closing this gap is the highest-leverage improvement.
Technology stack
Debian, on Apache, hosted on Apache HTTP Server
Stack Architecture
 Debian
 Open Graph
 Apache 2.2.22 Apache HTTP Server 2.2.22
All Detected Technologies (4)
Apache is a free and open-source cross-platform web server software.
Debian is a Linux software which is a free open-source software.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Observations (2)
Server version exposed in headers
The Server header reveals 'Apache 2.2.22'. Exposing exact server versions helps attackers target known vulnerabilities. Consider configuring your server to hide version information.
No build tool detected
A framework (Debian) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/gonetcrm.pl)<a href="https://beavercheck.com/sites/gonetcrm.pl"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fwww.gonetcrm.pl" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fwww.gonetcrm.plExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 6h total → projected A (92)
Sprint 1: Quick Wins
+4Highest ROI — low effort, high impact
- · HSTS header is missing
- · Cross-Origin-Opener-Policy header is missing
Sprint 2: Core Fixes
Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · Cross-Origin-Embedder-Policy header is missing
- · No DMARC record found