

Global Performance
6/6 locations ✓Acceptable global latency — average 251ms across 6 locations, fastest from New York (72ms), slowest from Singapore (485ms). Netlify edge cache ("Netlify Edge"; fwd=miss; fwd-status=200; stored).
Audit overview
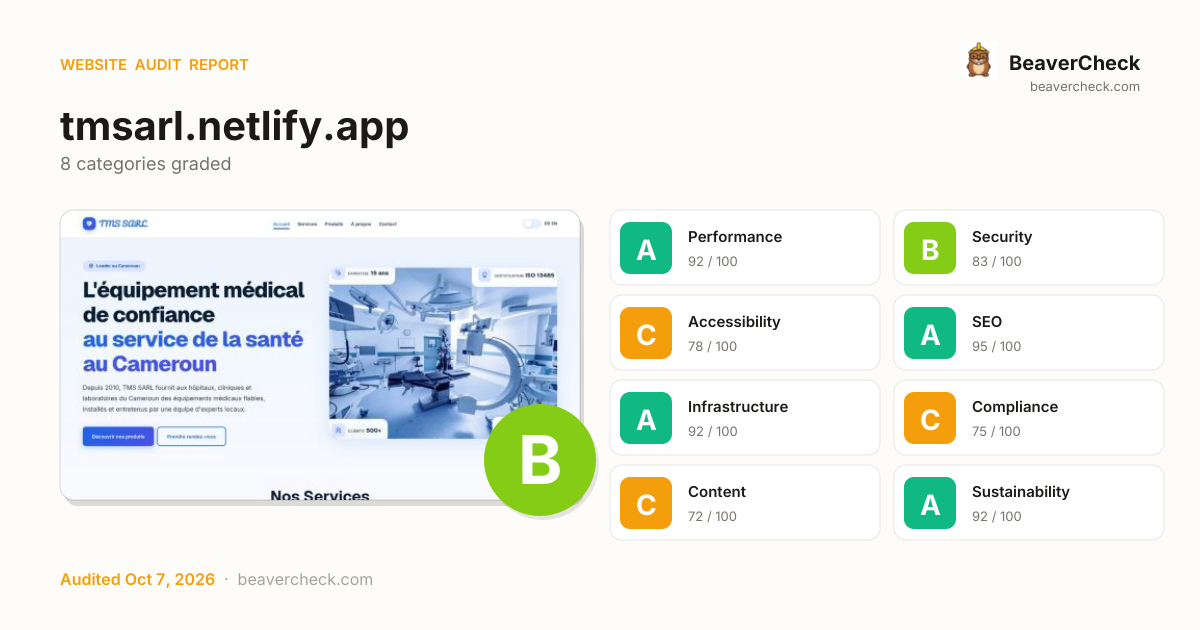
All categories sit comfortably above the 70 threshold; this is a clean audit.
Fix Priority Matrix
5 findingsQuick Wins
1High impact, low effort — start here.
Strategic
4High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
Screenshots
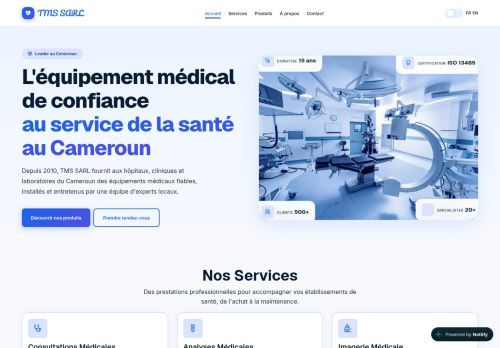
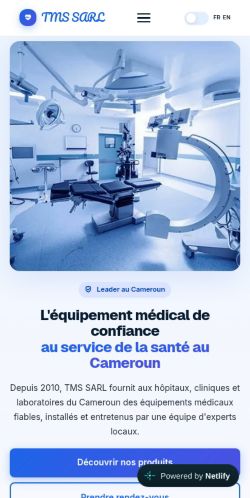
Your mail setup has problems.
tmsarl.netlify.app fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
'unsafe-eval' found in script source
Unsafe value (unsafe-inline, unsafe-eval) in script-src defeats CSP's main protection — XSS injections can execute again.
'unsafe-inline' found in script source
Unsafe value (unsafe-inline, unsafe-eval) in script-src defeats CSP's main protection — XSS injections can execute again.
69 inline style attribute(s) detected
Inline style attributes force `style-src 'unsafe-inline'` in any CSP -- effectively negating CSP's XSS-mitigation value for stylesheets.
7 third-party resources (46% of weight)
Informational: third-party resource count and their share of page weight. High share caps perf gains from frontend optimization.
Cross-Origin-Embedder-Policy header is missing
COEP enforces that all embedded resources opt-in to cross-origin embedding — required for cross-origin isolation features.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
$1,700 investment → $10,089/month returns + USD 150,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
6 barrier(s) likely increasing bounce by ~26%.
- Page takes 5.0s to loadUsers abandon at ~3s — you're 2.5s over the 2.5s threshold→ Optimize render-blocking resources, preload the hero image, and compress images
- No Open Graph tagsLinks shared on LinkedIn / Slack / Facebook show bare URLs — referral clicks drop→ Add og:title, og:description, og:image, og:url to the page head
- No structured dataNo rich-result eligibility in Google — lower SERP CTR vs competitors with stars and prices→ Add JSON-LD for your page type (Product, Article, FAQPage, LocalBusiness, …)
- Content is hard to readGraduate-level reading difficulty — limits the addressable audience for product or blog pages→ Shorten sentences; replace jargon with plain language; target Flesch ease ≥60
- No skip-to-content linkKeyboard and screen-reader users must tab through the entire header on every page→ Add a visible-on-focus <a href="#main">Skip to content</a> as the first focusable element
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
$150,000
- Skip navigation link is missing (WCAG 2.4.1)ADA Title III: USD 25,000 – USD 150,000
Bounce-Rate Cost
$7,061 /mo
+26.3pp bounce · ~2,625 lost visitors/mo
CPC: USD 2.69
Bandwidth Waste
$0.15 /mo
1906.4 MB/mo × 0.080 USD/GB
- Optimize transfer: save ~191 KB per page loadSaves $0.15/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 2 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
1.32 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
5.02 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
42 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.003
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.81 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
5.18 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
512 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
2.45 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.002
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
636 ms
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
2.45 s
Categories
8Performance
7 third-party resources (46% of weight)
Security
'unsafe-eval' found in script source
Accessibility
All checks pass
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of Bootstrap sites score 95+ on Content; you're at 72 — closing this gap is the highest-leverage improvement.
Top 10% of Google Font API sites score 95+ on Content; you're at 72 — closing this gap is the highest-leverage improvement.
Technology stack
Bootstrap, with Cloudflare CDN
Stack Architecture
 Bootstrap
 Google Font API
 Google Maps HSTS
 Cloudflare
 Netlify Netlify CDN
 cdnjs
All Detected Technologies (8)
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
Netlify providers hosting and server-less backend services for web applications and static websites.
cdnjs is a free distributed JS library delivery service.
Google Font API is a web service that supports open-source font files that can be used on your web designs.
Google Maps is a web mapping service. It offers satellite imagery, aerial photography, street maps, 360° interactive panoramic views of streets, real-time traffic conditions, and route planning for traveling by foot, car, bicycle and air, or public transportation.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
Observations (2)
No build tool detected
A framework (Bootstrap) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
8 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/tmsarl.netlify.app)<a href="https://beavercheck.com/sites/tmsarl.netlify.app"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Ftmsarl.netlify.app" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Ftmsarl.netlify.appExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
3 sprints · 17h total → projected A (91)
Sprint 1: Quick Wins
+1Highest ROI — low effort, high impact
- · 7 third-party resources (46% of weight)
Sprint 2: Core Fixes
+2Medium effort, high structural impact
- · Cross-Origin-Embedder-Policy header is missing
- · 69 inline style attribute(s) detected
Sprint 3: Strategic Improvements
+2Higher effort, long-term payoff
- · 'unsafe-eval' found in script source
- · 'unsafe-inline' found in script source