

Global Performance
6/6 locations ✓Strong global performance — average 186ms across 6 locations, fastest from Singapore (16ms), slowest from Madrid (519ms). No CDN (document or assets). 1 location above the 500ms target.
Audit overview
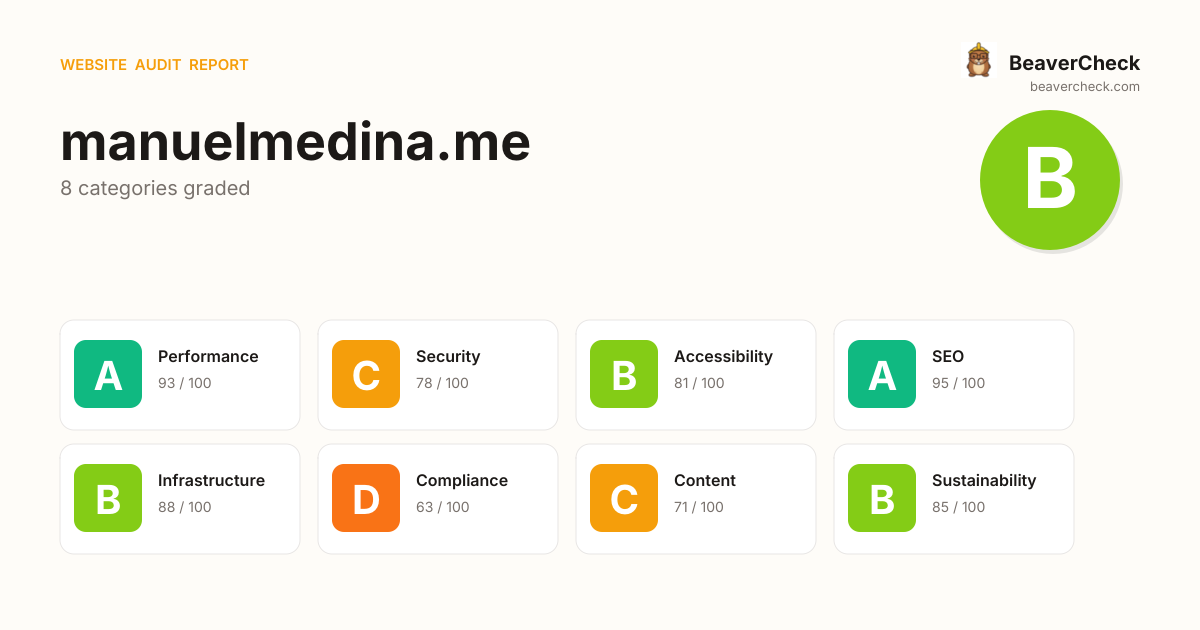
Compliance needs attention; the rest of the categories are in good shape.
Fix Priority Matrix
5 findingsQuick Wins
1High impact, low effort — start here.
Strategic
4High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
Screenshots
Your mail setup has problems.
manuelmedina.me fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
10 render-blocking <script src> tag(s) without async/defer
Performance issues directly impact user engagement and conversion rates.
69 inline style attribute(s) detected
Inline style attributes force `style-src 'unsafe-inline'` in any CSP -- effectively negating CSP's XSS-mitigation value for stylesheets.
Cross-Origin-Embedder-Policy header is missing
COEP enforces that all embedded resources opt-in to cross-origin embedding — required for cross-origin isolation features.
Cross-Origin-Opener-Policy header is missing
COOP isolates your top-level browsing context from cross-origin windows — without it, popup-based side-channel attacks remain possible.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
$1,025 investment → $1,598/month returns + USD 157,500 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
6 barrier(s) likely increasing bounce by ~14%.
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
- No Open Graph tagsLinks shared on LinkedIn / Slack / Facebook show bare URLs — referral clicks drop→ Add og:title, og:description, og:image, og:url to the page head
- No structured dataNo rich-result eligibility in Google — lower SERP CTR vs competitors with stars and prices→ Add JSON-LD for your page type (Product, Article, FAQPage, LocalBusiness, …)
- Content is hard to readGraduate-level reading difficulty — limits the addressable audience for product or blog pages→ Shorten sentences; replace jargon with plain language; target Flesch ease ≥60
- No skip-to-content linkKeyboard and screen-reader users must tab through the entire header on every page→ Add a visible-on-focus <a href="#main">Skip to content</a> as the first focusable element
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
$157,500
- No privacy policy found (page links and common paths checked)CCPA/CPRA: USD 2,500 – USD 7,500
- Trackers detected but no cookie policy foundCCPA/CPRA: USD 2,500 – USD 7,500
- Trackers detected but no privacy policy foundCCPA/CPRA: USD 2,500 – USD 7,500
Bounce-Rate Cost
$1,598 /mo
+13.8pp bounce · ~1,377 lost visitors/mo
CPC: USD 1.16
Bandwidth Waste
$0.12 /mo
1469.8 MB/mo × 0.080 USD/GB
- Optimize transfer: save ~147 KB per page loadSaves $0.12/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 1 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Categories
8Performance
10 render-blocking <script src> tag(s) without async/defer
Security
Content-Security-Policy header is missing
Accessibility
All checks pass
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of WordPress sites score 85+ on Compliance; you're at 63 — closing this gap is the highest-leverage improvement.
Technology stack
WordPress, on PHP, hosted on wp.cloud, with Nginx CDN
Stack Architecture
 Gauges
 Jetpack Boost
 WooCommerce
 WordPress
 Bulma Google Search Console HSTS
 MySQL
 Priority Hints
 RSS Twitter Emoji (Twemoji)
 core-js 3.39.0
 jQuery 3.7.1 jQuery Migrate 3.4.1
 PHP
 Nginx
 wp.cloud
All Detected Technologies (17)
Nginx is a web server that can also be used as a reverse proxy, load balancer, mail proxy and HTTP cache.
WordPress-first cloud hosting.
PHP is a general-purpose scripting language used for web development.
WordPress is a free and open-source content management system written in PHP and paired with a MySQL or MariaDB database. Features include a plugin architecture and a template system.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
MySQL is an open-source relational database management system.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
RSS is a family of web feed formats used to publish frequently updated works—such as blog entries, news headlines, audio, and video—in a standardized format.
Twitter Emoji is a set of open-source emoticons and emojis for Twitter, TweetDeck, and also for Android and iOS versions of the application.
core-js is a modular standard library for JavaScript, with polyfills for cutting-edge ECMAScript features.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
Query Migrate is a javascript library that allows you to preserve the compatibility of your jQuery code developed for versions of jQuery older than 1.9.
Gauges is a real-time web analytics tool that provides live traffic updates and essential metrics for websites.
Jetpack Boost – Website Speed, Performance and Critical CSS.
Observations (3)
WordPress detected — review security configuration
WordPress sites benefit from: protecting wp-login.php, disabling XML-RPC if unused, restricting REST API access, and keeping all plugins and themes up to date. Check the Security tab for specific findings.
No build tool detected
A framework (Bulma) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
17 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/manuelmedina.me)<a href="https://beavercheck.com/sites/manuelmedina.me"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fmanuelmedina.me" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fmanuelmedina.meExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 10h total → projected B (89)
Sprint 1: Quick Wins
+1Highest ROI — low effort, high impact
- · Cross-Origin-Opener-Policy header is missing
Sprint 2: Core Fixes
+5Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · Cross-Origin-Embedder-Policy header is missing
- · 10 render-blocking <script src> tag(s) without async/defer
- · 69 inline style attribute(s) detected