
Audit overview
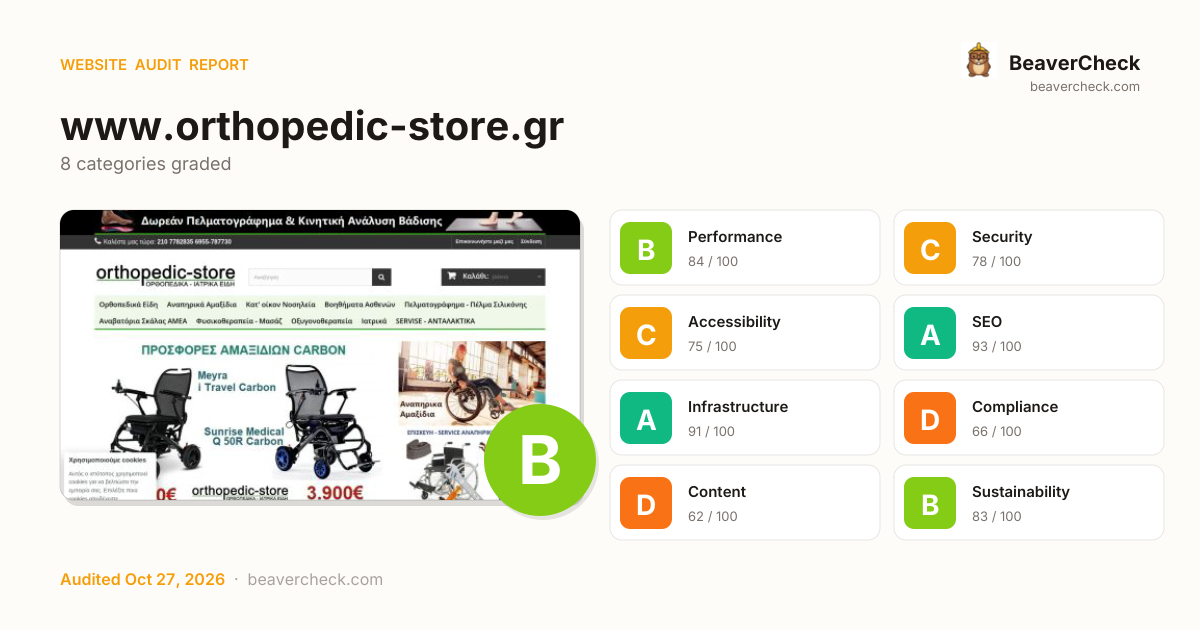
Compliance and Content need attention; the other categories are in good shape.
Fix Priority Matrix
5 findingsQuick Wins
3High impact, low effort — start here.
Strategic
2High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
Screenshots
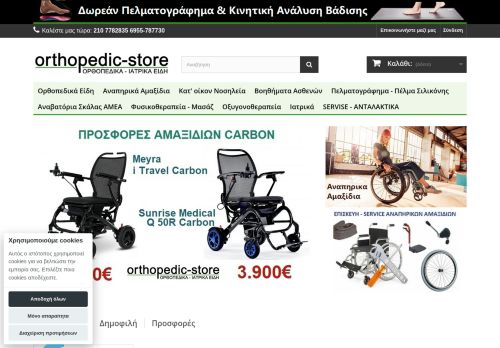
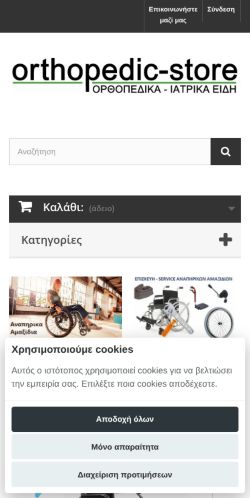
Your mail setup has problems.
orthopedic-store.gr fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
48 link(s) with no accessible text
Links with no accessible text (empty <a></a>, image-only no alt, icon-only no aria-label) are unidentifiable to screen readers.
No <main> landmark found
Without a <main> landmark, screen-reader users can't skip past the navigation to the page content — every page starts with re-reading the menu.
No H1 heading found
No H1 means screen-reader users can't identify the page's primary topic, and Google's content-extraction degrades.
11 inline style attribute(s) detected
Inline style attributes force `style-src 'unsafe-inline'` in any CSP -- effectively negating CSP's XSS-mitigation value for stylesheets.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
€313 investment → €4,509/month returns + EUR 120,500,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
10 barrier(s) likely increasing bounce by ~25%.
- 24 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
- Page loads in 3.7sEvery additional 100ms above 2.5s costs conversions — you're 1.2s over→ Target <2.5s LCP: defer non-critical scripts and optimize the hero image
- High main-thread blocking timePage is non-interactive for 316ms after first paint→ Defer third-party scripts and split large bundles
- HSTS is enabled but max-age is short (15768000s)First-visit protection is in place, but browsers forget the policy sooner than recommended→ Raise Strict-Transport-Security max-age to at least 31536000 (1 year)
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
€120.500.000
- No privacy policy found (page links and common paths checked)GDPR: EUR 10.000 – EUR 20.000.000
- Trackers detected but no cookie policy foundGDPR: EUR 5.000 – EUR 10.000.000
- Trackers detected but no cookie policy foundGDPR: EUR 10.000 – EUR 20.000.000
Bounce-Rate Cost
€2.704 /mo
+25.2pp bounce · ~2,517 lost visitors/mo
CPC: EUR 1.07
Bandwidth Waste
€0,68 /mo
9164.6 MB/mo × 0.074 EUR/GB
- Optimize transfer: save ~916 KB per page loadSaves €0,68/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 4 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
2.39 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
3.67 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
316 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.058
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
4.02 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
9.61 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
879 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.69 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
3 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.104
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.19 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
2.67 s
Categories
8Performance
All checks pass
Security
Content-Security-Policy header is missing
Accessibility
48 link(s) with no accessible text
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of Cart Functionality sites score 94+ on Content; you're at 62 — closing this gap is the highest-leverage improvement.
Technology stack
Bootstrap, on PHP, with Cloudflare CDN
Stack Architecture
 Google Analytics
 Google Tag Manager
 Zendesk Chat
 Cart Functionality
 PrestaShop
 Bootstrap
 FancyBox 2.1.5
 Google Font API HSTS
 HTTP/3
 MySQL
 Zendesk Widget
 jQuery 1.11.0 jQuery Migrate
 reCAPTCHA
 PHP 5.6.40
 Cloudflare
 jsDelivr jsDelivr CDN
All Detected Technologies (19)
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
JSDelivr is a free public CDN for open-source projects. It can serve web files directly from the npm registry and GitHub repositories without any configuration.
PHP is a general-purpose scripting language used for web development.
Websites that have a shopping cart or checkout page, either using a known ecommerce platform or a custom solution.
PrestaShop is a freemium, open-source ecommerce solution, written in the PHP programming language with support for the MySQL database management system.
FancyBox is a tool for displaying images, html content and multi-media in a Mac-style 'lightbox' that floats overtop of web page.
Google Font API is a web service that supports open-source font files that can be used on your web designs.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
MySQL is an open-source relational database management system.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
Query Migrate is a javascript library that allows you to preserve the compatibility of your jQuery code developed for versions of jQuery older than 1.9.
reCAPTCHA is a free service from Google that helps protect websites from spam and abuse.
Google Analytics is a free web analytics service that tracks and reports website traffic.
Google Tag Manager is a tag management system (TMS) that allows you to quickly and easily update measurement codes and related code fragments collectively known as tags on your website or mobile app.
Zendesk Chat is a live chat and communication widget.
Observations (5)
Runtime exposed via X-Powered-By header
The X-Powered-By header reveals 'PHP 5.6.40'. Remove this header in production to reduce information leakage.
No build tool detected
A framework (Bootstrap) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
jQuery version may be outdated
Detected jQuery 1.11.0. The current major version is 3. Consider updating for security patches and new features.
PHP version may be outdated
Detected PHP 5.6.40. The current major version is 8. Consider updating for security patches and new features.
Complex technology stack detected
19 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/orthopedic-store.gr)<a href="https://beavercheck.com/sites/orthopedic-store.gr"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fwww.orthopedic-store.gr" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fwww.orthopedic-store.grExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 8h total → projected B (87)
Sprint 1: Quick Wins
+4Highest ROI — low effort, high impact
- · No <main> landmark found
- · No H1 heading found
- · 48 link(s) with no accessible text
Sprint 2: Core Fixes
+3Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · 11 inline style attribute(s) detected