
Global Performance
6/6 locations ✓Acceptable global latency — average 328ms across 6 locations, fastest from Amsterdam (71ms), slowest from Singapore (809ms). Vercel edge cache (HIT). 2 locations above the 500ms target.
Audit overview
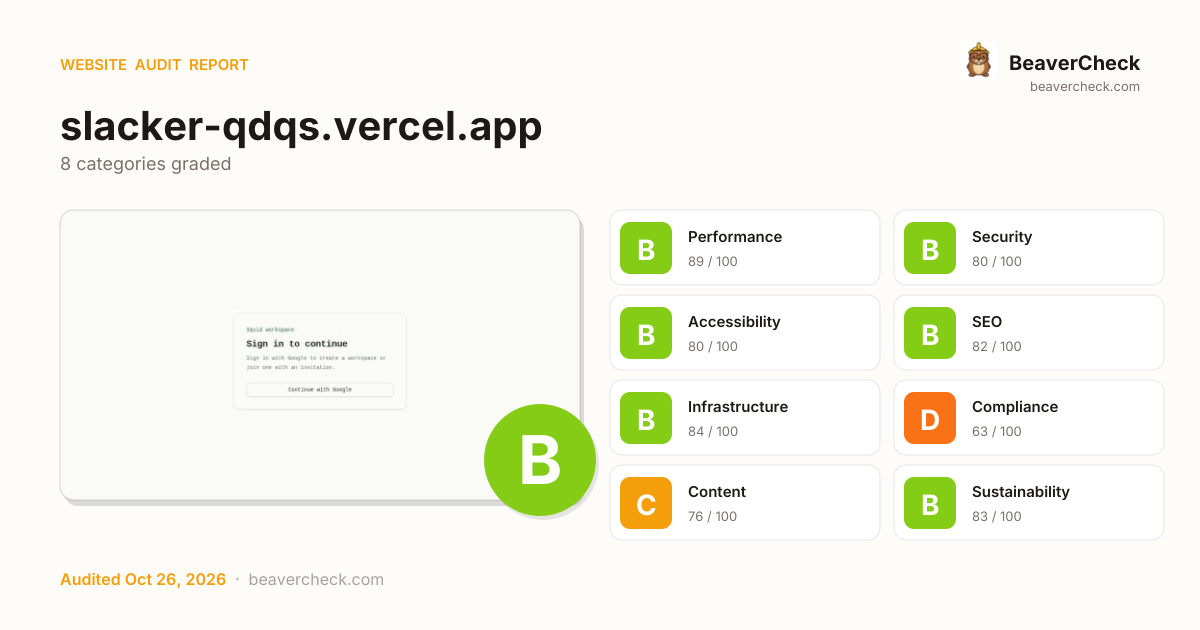
Compliance needs attention; the rest of the categories are in good shape.
Fix Priority Matrix
5 findingsQuick Wins
2High impact, low effort — start here.
Strategic
3High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
Screenshots
Your mail setup has problems.
slacker-qdqs.vercel.app fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
Page body has only 177 chars of text -- likely empty / placeholder
Security gaps expose your site and users to attacks, eroding trust.
Cross-Origin-Embedder-Policy header is missing
COEP enforces that all embedded resources opt-in to cross-origin embedding — required for cross-origin isolation features.
Cross-Origin-Opener-Policy header is missing
COOP isolates your top-level browsing context from cross-origin windows — without it, popup-based side-channel attacks remain possible.
No DMARC record found
Without DMARC, anyone can send phishing emails using your domain name.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
$575 investment → $9,118/month returns + USD 157,500 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
8 barrier(s) likely increasing bounce by ~25%.
- Page feels frozen for 944msClicks on the primary CTA are ignored while JavaScript runs→ Break up long tasks; defer non-critical JavaScript to post-hydration
- Page loads in 3.9sEvery additional 100ms above 2.5s costs conversions — you're 1.4s over→ Target <2.5s LCP: defer non-critical scripts and optimize the hero image
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
- No Open Graph tagsLinks shared on LinkedIn / Slack / Facebook show bare URLs — referral clicks drop→ Add og:title, og:description, og:image, og:url to the page head
- No structured dataNo rich-result eligibility in Google — lower SERP CTR vs competitors with stars and prices→ Add JSON-LD for your page type (Product, Article, FAQPage, LocalBusiness, …)
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
$157,500
- No privacy policy found (page links and common paths checked)CCPA/CPRA: USD 2,500 – USD 7,500
- Privacy Policy not detectedCCPA/CPRA: USD 2,500 – USD 7,500
- No <nav> landmark foundADA Title III: USD 25,000 – USD 150,000
Bounce-Rate Cost
$6,771 /mo
+25.2pp bounce · ~2,517 lost visitors/mo
CPC: USD 2.69
Bandwidth Waste
$0.23 /mo
2902.8 MB/mo × 0.080 USD/GB
- Optimize transfer: save ~290 KB per page loadSaves $0.23/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 2 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
1.44 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
3.90 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
944 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.44 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
4.26 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
343 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
760 ms
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
78 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
343 ms
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
849 ms
Categories
8Performance
All checks pass
Security
Content-Security-Policy header is missing
Accessibility
All checks pass
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of HSTS sites score 87+ on Compliance; you're at 63 — closing this gap is the highest-leverage improvement.
Technology stack
HSTS, hosted on Vercel, with Vercel Edge CDN
Stack Architecture
 Vercel Edge Vercel
All Detected Technologies (3)
Vercel is a cloud platform for static frontends and serverless functions.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
Observations (1)
No build tool detected
A framework (HSTS) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/slacker-qdqs.vercel.app)<a href="https://beavercheck.com/sites/slacker-qdqs.vercel.app"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fslacker-qdqs.vercel.app" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fslacker-qdqs.vercel.appExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 6h total → projected B (86)
Sprint 1: Quick Wins
+4Highest ROI — low effort, high impact
- · Page body has only 177 chars of text -- likely empty / placeholder
- · Cross-Origin-Opener-Policy header is missing
Sprint 2: Core Fixes
+1Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · Cross-Origin-Embedder-Policy header is missing
- · No DMARC record found