

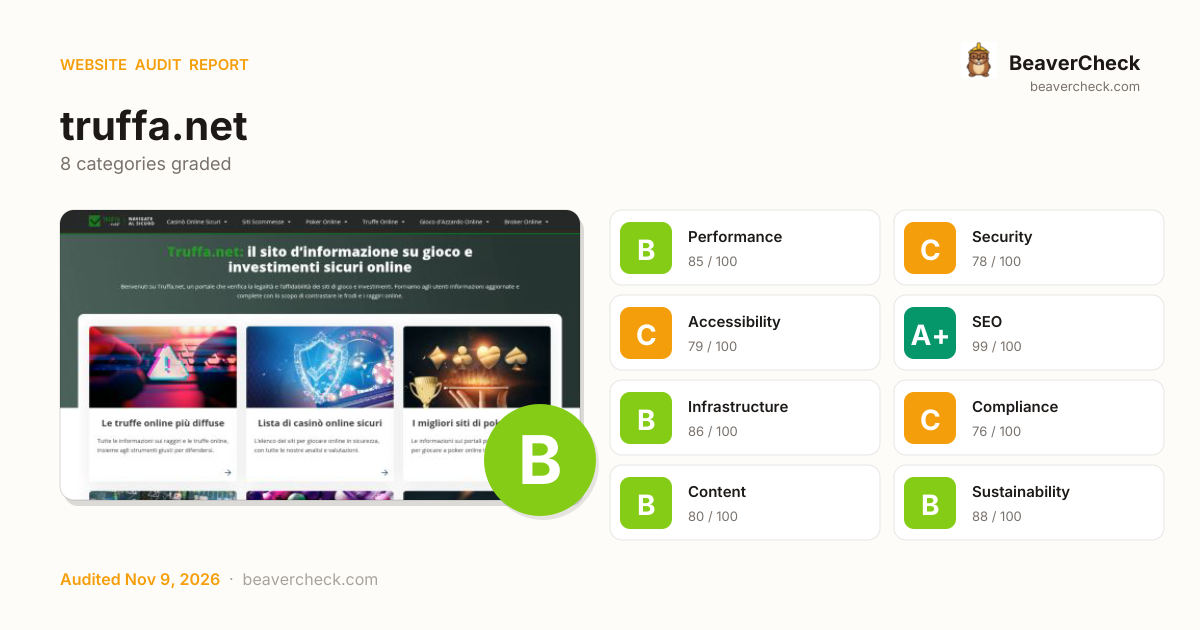
Audit overview
All categories sit comfortably above the 70 threshold; this is a clean audit.
Fix Priority Matrix
5 findingsQuick Wins
3High impact, low effort — start here.
Strategic
2High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
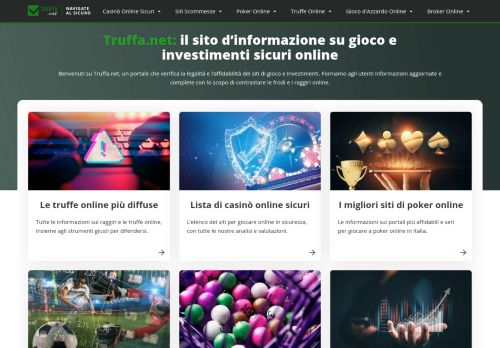
Screenshots
Your mail setup has problems.
truffa.net fails 2 mail checks: No DMARC record found, No SPF record found. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
Cookie 'PHPSESSID' is missing the Secure flag
A cookie without the Secure flag can leak over HTTP — in HSTS-protected sites, this is still a defense-in-depth gap.
Cookie 'cntctfrm_send_mail' is missing the Secure flag
A cookie without the Secure flag can leak over HTTP — in HSTS-protected sites, this is still a defense-in-depth gap.
1 image(s) missing alt attribute
Each image without alt text is a WCAG 1.1.1 failure — invisible to screen-reader users, lost from Google Image Search.
4 link(s) with no accessible text
Links with no accessible text (empty <a></a>, image-only no alt, icon-only no aria-label) are unidentifiable to screen readers.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
€468 investment → €2,852/month returns + EUR 500,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
4 barrier(s) likely increasing bounce by ~13%.
- 37 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
- Content is hard to readGraduate-level reading difficulty — limits the addressable audience for product or blog pages→ Shorten sentences; replace jargon with plain language; target Flesch ease ≥60
- No skip-to-content linkKeyboard and screen-reader users must tab through the entire header on every page→ Add a visible-on-focus <a href="#main">Skip to content</a> as the first focusable element
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
€500.000
- No <nav> landmark foundEAA: EUR 1.000 – EUR 500.000
- Skip navigation link is missing (WCAG 2.4.1)EAA: EUR 1.000 – EUR 500.000
- 1 image(s) missing alt attributeEAA: EUR 1.000 – EUR 500.000
Bounce-Rate Cost
€2.851 /mo
+13.0pp bounce · ~1,296 lost visitors/mo
CPC: EUR 2.20
Bandwidth Waste
€0,53 /mo
7213.4 MB/mo × 0.074 EUR/GB
- Optimize transfer: save ~721 KB per page loadSaves €0,53/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 5 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
2.75 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
0 ms
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
5.08 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
0 ms
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
929 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.36 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
8 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.006
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.71 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
2.82 s
Categories
8Performance
All checks pass
Security
Content-Security-Policy header is missing
Accessibility
1 image(s) missing alt attribute
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of WordPress sites score 96+ on Content; you're at 80 — closing this gap is the highest-leverage improvement.
Top 10% of Cloudflare Bot Management sites score 98+ on Infrastructure; you're at 86 — closing this gap is the highest-leverage improvement.
Technology stack
WordPress, on PHP, with Cloudflare CDN
Stack Architecture
 WordPress
 Cloudflare Bot Management
 DataTables 1.10.18
 Elfsight HSTS
 HTTP/3
 LazySizes
 Open Graph
 Priority Hints
 React
 Swiper
 jQuery 3.6.0
 PHP
 styled-components 6.5.3 Cloudflare
All Detected Technologies (15)
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
PHP is a general-purpose scripting language used for web development.
Styled components is a CSS-in-JS styling framework that uses tagged template literals in JavaScript.
Cloudflare bot management solution identifies and mitigates automated traffic to protect websites from bad bots.
DataTables is a plug-in for the jQuery Javascript library adding advanced features like pagination, instant search, themes, and more to any HTML table.
Elfsight is an all-in-one platform offering 70+ customisable widgets for websites.
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
LazySizes is a JavaScript library used to delay the loading of images (iframes, scripts, etc) until they come into view.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
React is an open-source JavaScript library for building user interfaces or UI components.
Swiper is a JavaScript library that creates modern touch sliders with hardware-accelerated transitions.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
Observations (5)
Runtime exposed via X-Powered-By header
The X-Powered-By header reveals 'styled-components 6.5.3'. Remove this header in production to reduce information leakage.
WordPress detected — review security configuration
WordPress sites benefit from: protecting wp-login.php, disabling XML-RPC if unused, restricting REST API access, and keeping all plugins and themes up to date. Check the Security tab for specific findings.
jQuery loaded alongside a modern framework
Both jQuery and React are loaded. Modern frameworks handle DOM manipulation natively. jQuery may be unnecessary and adds ~30KB to the page weight. Check the Performance tab for bundle analysis.
No build tool detected
A framework (Cloudflare Bot Management) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
15 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/truffa.net)<a href="https://beavercheck.com/sites/truffa.net"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Ftruffa.net" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Ftruffa.netExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 6h total → projected A (91)
Sprint 1: Quick Wins
+6Highest ROI — low effort, high impact
- · Cookie 'PHPSESSID' is missing the Secure flag
- · Cookie 'cntctfrm_send_mail' is missing the Secure flag
- · 4 link(s) with no accessible text
Sprint 2: Core Fixes
+2Medium effort, high structural impact
- · 1 image(s) missing alt attribute
- · Content-Security-Policy header is missing