

Audit overview
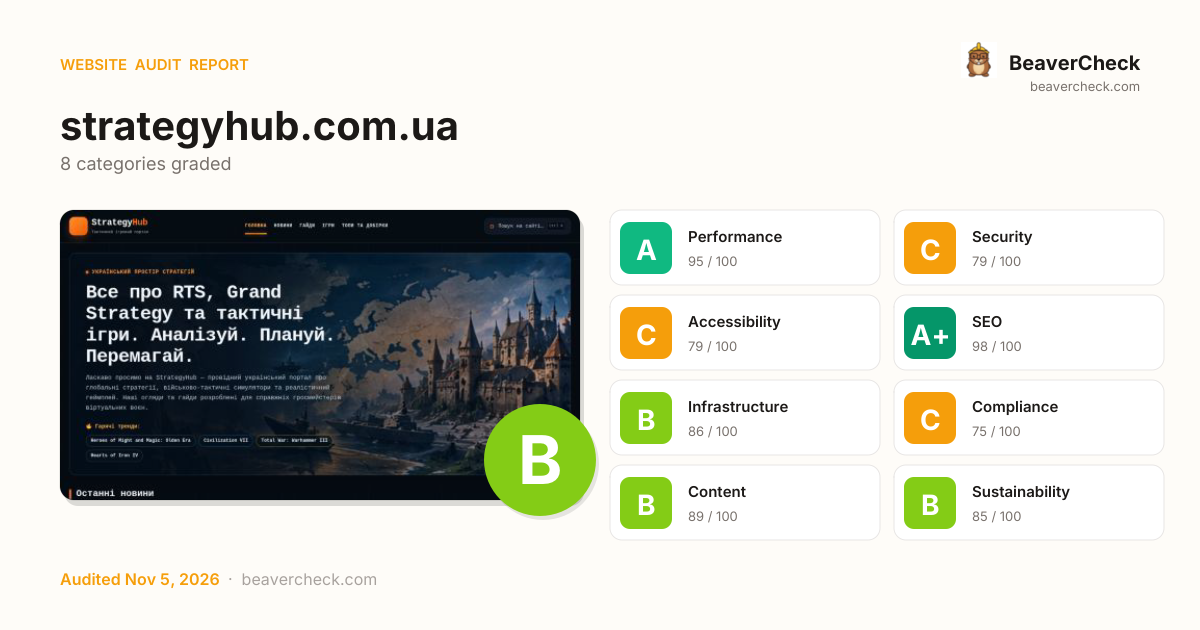
All categories sit comfortably above the 70 threshold; this is a clean audit.
Fix Priority Matrix
5 findingsQuick Wins
2High impact, low effort — start here.
Strategic
3High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
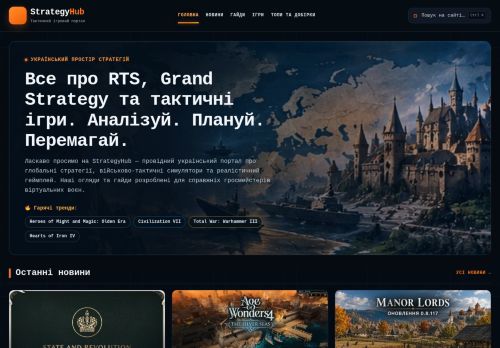
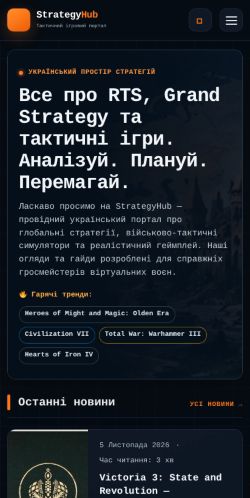
Screenshots
Your mail setup has problems.
strategyhub.com.ua fails 1 mail check: DMARC policy is none — monitoring only. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
HSTS header is missing
Without HSTS, a network attacker can downgrade the very first connection to HTTP and steal the user's session.
1 software version(s) disclosed in HTML: Site Kit by Google 1.179.0
Each disclosed version enables direct CVE lookup -- attacker reads the version, searches the CVE database, targets the site with a tested exploit.
4 render-blocking <script src> tag(s) without async/defer
Performance issues directly impact user engagement and conversion rates.
Cross-Origin-Embedder-Policy header is missing
COEP enforces that all embedded resources opt-in to cross-origin embedding — required for cross-origin isolation features.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
₴7,800 investment → ₴248,790/month returns
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
5 barrier(s) likely increasing bounce by ~18%.
- 4 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
- Page loads in 3.2sEvery additional 100ms above 2.5s costs conversions — you're 659ms over→ Target <2.5s LCP: defer non-critical scripts and optimize the hero image
- No HSTS headerReturning visitors are briefly exposed to downgrade attacks on first request→ Set Strict-Transport-Security: max-age=31536000; includeSubDomains
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
- No skip-to-content linkKeyboard and screen-reader users must tab through the entire header on every page→ Add a visible-on-focus <a href="#main">Skip to content</a> as the first focusable element
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Bounce-Rate Cost
₴197,074 /mo
+17.6pp bounce · ~1,758 lost visitors/mo
CPC: UAH 112.08
Bandwidth Waste
₴2.41 /mo
721.8 MB/mo × 3.333 UAH/GB
- Optimize transfer: save ~72 KB per page loadSaves ₴2.41/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 2 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
2.12 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
3.16 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
69 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
4.58 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
3.16 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
745 ms
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.07 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
0 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
883 ms
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
1.07 s
Categories
8Performance
4 render-blocking <script src> tag(s) without async/defer
Security
Content-Security-Policy header is missing
Accessibility
All checks pass
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Top 10% of WordPress sites score 97+ on Infrastructure; you're at 86 — closing this gap is the highest-leverage improvement.
Technology stack
WordPress, on Apache, hosted on Apache HTTP Server
Stack Architecture
 WordPress
 AddToAny
 Google Font API
 Open Graph
 Priority Hints
 RSS Twitter Emoji (Twemoji)
 jQuery 3.7.1
 Apache Apache HTTP Server
All Detected Technologies (10)
Apache is a free and open-source cross-platform web server software.
AddToAny is a universal sharing platform that can be integrated into a website by use of a web widget or plugin.
Google Font API is a web service that supports open-source font files that can be used on your web designs.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
RSS is a family of web feed formats used to publish frequently updated works—such as blog entries, news headlines, audio, and video—in a standardized format.
Twitter Emoji is a set of open-source emoticons and emojis for Twitter, TweetDeck, and also for Android and iOS versions of the application.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
Observations (3)
WordPress detected — review security configuration
WordPress sites benefit from: protecting wp-login.php, disabling XML-RPC if unused, restricting REST API access, and keeping all plugins and themes up to date. Check the Security tab for specific findings.
No build tool detected
A framework (AddToAny) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
10 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/strategyhub.com.ua)<a href="https://beavercheck.com/sites/strategyhub.com.ua"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fstrategyhub.com.ua" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fstrategyhub.com.uaExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 6h total → projected A (92)
Sprint 1: Quick Wins
+3Highest ROI — low effort, high impact
- · HSTS header is missing
- · 1 software version(s) disclosed in HTML: Site Kit by Google 1.179.0
Sprint 2: Core Fixes
+3Medium effort, high structural impact
- · Content-Security-Policy header is missing
- · Cross-Origin-Embedder-Policy header is missing
- · 4 render-blocking <script src> tag(s) without async/defer