

Global Performance
6/6 locations ✓High global latency — average 4014ms across 6 locations, fastest from Madrid (297ms), slowest from Singapore (10835ms). Cloudflare edge cache (DYNAMIC). 5 locations above the 500ms target.
Audit overview
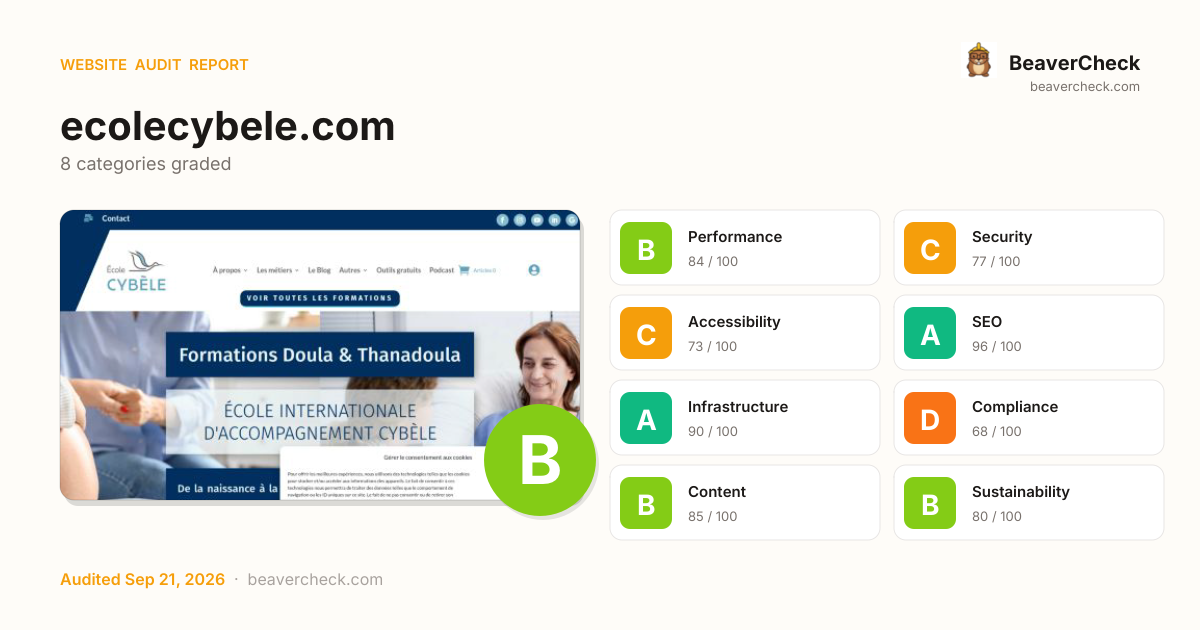
Compliance needs attention; the rest of the categories are in good shape.
Fix Priority Matrix
5 findingsQuick Wins
4High impact, low effort — start here.
Strategic
1High impact, requires investment.
Easy Improvements
0Small gains, minimal effort.
Nothing in this quadrant — good news.
Deprioritize
0Low impact, high effort — do last.
Nothing in this quadrant — good news.
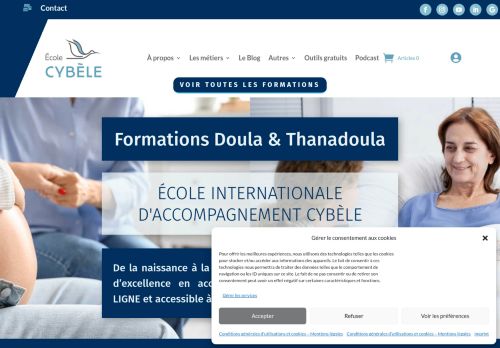
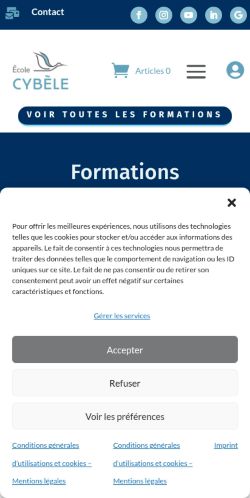
Screenshots
Your mail setup has problems.
ecolecybele.com fails 1 mail check: DMARC policy is none — monitoring only. This is the kind of misconfiguration that sends your mail to spam.
Top Priorities (5)
Content-Security-Policy header is missing
Without a CSP, a single XSS bug can exfiltrate everything your users type — including credentials.
HSTS header is missing
Without HSTS, a network attacker can downgrade the very first connection to HTTP and steal the user's session.
1 image-in-link without alt text
Image-only links with no alt create empty links — screen-reader users hear 'link' with no destination context.
1 link(s) with no accessible text
Links with no accessible text (empty <a></a>, image-only no alt, icon-only no aria-label) are unidentifiable to screen readers.
4 button(s) with no accessible text
Buttons with no accessible text (icon-only, no aria-label) can't be activated by voice control or understood by screen readers.
Business case
What fixing the audit's findings is worth -- and what ignoring them keeps costing.
Return on investment
€380 investment → €2,523/month returns + EUR 120,500,000 risk avoided
Figures combine localized regulatory fine ceilings, search/conversion value priced against local CPC, and bandwidth waste estimates. Results depend on implementation quality and audience composition. Not legal or financial advice.
Conversion barriers
7 barrier(s) likely increasing bounce by ~30%.
- Page takes 20.7s to loadUsers abandon at ~3s — you're 18.2s over the 2.5s threshold→ Optimize render-blocking resources, preload the hero image, and compress images
- Page feels frozen for 1.4sClicks on the primary CTA are ignored while JavaScript runs→ Break up long tasks; defer non-critical JavaScript to post-hydration
- 5 broken link(s) on the pageClicks land on 404s — trust drops and the session often ends→ Fix or remove the broken destinations surfaced on the Content tab
- No HSTS headerReturning visitors are briefly exposed to downgrade attacks on first request→ Set Strict-Transport-Security: max-age=31536000; includeSubDomains
- No Content-Security-Policy headerHigher XSS blast radius — one compromised script can exfiltrate the checkout form→ Ship a reporting-only CSP first, then enforce once violations are clean
Preliminary CRO audit — each barrier links to the tab with detailed analysis.
Remediation cost
Start here for the best return on investment
Cost by category
Cost by effort level
Adjust assumptions
Team composition
Multiplier applied to dev hours to reflect QA, design, and PM overhead. Use Dev only for solo work; Full team for projects with formal review processes.
Rates reflect fully-loaded developer cost including overhead
Warning:Cost of inaction
Compliance Risk
€120.500.000
- Trackers detected but no cookie policy foundRGPD: EUR 5.000 – EUR 10.000.000
- Trackers detected but no cookie policy foundRGPD: EUR 10.000 – EUR 20.000.000
- Trackers detected but no cookie policy foundePrivacy Directive: EUR 5.000 – EUR 100.000.000
Bounce-Rate Cost
€2.522 /mo
+29.7pp bounce · ~2,967 lost visitors/mo
CPC: EUR 0.85
Bandwidth Waste
€0,69 /mo
9369.2 MB/mo × 0.074 EUR/GB
- Optimize transfer: save ~937 KB per page loadSaves €0,69/mo
Compliance figures represent the statutory maximum fine for the most severe triggered category, capped per regulation — not the sum of per-finding penalties. Based on published regulatory fine ranges. This is not legal advice.
Unique monthly visitors from your analytics
Purchases, signups, or key actions
Optional — for revenue estimation
more engaged visitors from reduced bounce
Fix 5 critical issues to capture this value
How this is calculated
Based on Google/Deloitte research ("Milliseconds Make Millions") showing a ~7% bounce rate increase per additional second of LCP above the 2.5s "Good" threshold.
Your site's LCP: → estimated after fixes.
These are estimates based on industry research — actual results vary
Your data stays in your browser — nothing is sent to our servers
Lighthouse
Mobile
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
7.32 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
20.72 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
1.44 s
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.000
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
11.67 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
20.74 s
Desktop
First Contentful Paint First Contentful Paint — how long until the browser renders the first piece of content. Under 1.8s is good.
1.40 s
Largest Contentful Paint Largest Contentful Paint — how long until the largest visible element loads. Under 2.5s is good.
1.62 s
Total Blocking Time Total Blocking Time — total time the main thread was blocked, preventing user input. Under 200ms is good.
5 ms
Cumulative Layout Shift Cumulative Layout Shift — measures visual stability. How much the page layout shifts during loading. Under 0.1 is good.
0.007
Speed Index Speed Index — how quickly content is visually displayed during load. Under 3.4s is good.
1.57 s
Time to Interactive Time to Interactive — how long until the page is fully interactive and responds to user input. Under 3.8s is good.
4.11 s
Categories
8Performance
All checks pass
Security
Content-Security-Policy header is missing
Accessibility
1 image-in-link without alt text
SEO
All checks pass
Infrastructure
All checks pass
Compliance
All checks pass
Content
All checks pass
Sustainability
All checks pass
How you compare
Where this site stands against peers running the same stack.
Technology stack
Divi 5.13, on PHP, with Cloudflare CDN
Stack Architecture
 ActiveCampaign
 Google Analytics
 Google Tag Manager
 WP Courseware
 WP Rocket
 Yoast SEO
 WooCommerce
 Divi 5.13
 WordPress
 Complianz 7.6.5
 Google Font API Google Search Console Google Workspace
 HTTP/3
 Lodash 1.13.8
 MySQL
 Open Graph
 Priority Hints
 RSS
 React 18.3.1
 Swiper
 core-js 3.26.1
 jQuery 3.7.1 jQuery Migrate 3.4.1
 jQuery UI 1.14.2
 PHP
 Cloudflare
 jsDelivr
All Detected Technologies (28)
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
JSDelivr is a free public CDN for open-source projects. It can serve web files directly from the npm registry and GitHub repositories without any configuration.
PHP is a general-purpose scripting language used for web development.
Divi is a WordPress Theme and standalone WordPress plugin from Elegant themes that allows users to build websites using the visual drag-and-drop Divi page builder.
WordPress is a free and open-source content management system written in PHP and paired with a MySQL or MariaDB database. Features include a plugin architecture and a template system.
WooCommerce is an open-source ecommerce plugin for WordPress.
Complianz is a GDPR/CCPA Cookie Consent plugin that supports GDPR, DSGVO, CCPA and PIPEDA with a conditional Cookie Notice and customized Cookie Policy based on the results of the built-in Cookie Scan.
Google Font API is a web service that supports open-source font files that can be used on your web designs.
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
Lodash is a JavaScript library which provides utility functions for common programming tasks using the functional programming paradigm.
MySQL is an open-source relational database management system.
Open Graph is a protocol that is used to integrate any web page into the social graph.
Priority Hints exposes a mechanism for developers to signal a relative priority for browsers to consider when fetching resources.
RSS is a family of web feed formats used to publish frequently updated works—such as blog entries, news headlines, audio, and video—in a standardized format.
React is an open-source JavaScript library for building user interfaces or UI components.
Swiper is a JavaScript library that creates modern touch sliders with hardware-accelerated transitions.
core-js is a modular standard library for JavaScript, with polyfills for cutting-edge ECMAScript features.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
Query Migrate is a javascript library that allows you to preserve the compatibility of your jQuery code developed for versions of jQuery older than 1.9.
jQuery UI is a collection of GUI widgets, animated visual effects, and themes implemented with jQuery, Cascading Style Sheets, and HTML.
ActiveCampaign is email and marketing automation software.
Google Analytics is a free web analytics service that tracks and reports website traffic.
Google Tag Manager is a tag management system (TMS) that allows you to quickly and easily update measurement codes and related code fragments collectively known as tags on your website or mobile app.
WP Courseware is an LMS plugin that allows novice and professional users to build online courses using its easy-to-use drag and drop course builder.
WP Rocket is a caching and performance optimisation plugin to improve the loading speed of WordPress websites.
Yoast SEO is a search engine optimisation plugin for WordPress and other platforms.
Observations (4)
WordPress detected — review security configuration
WordPress sites benefit from: protecting wp-login.php, disabling XML-RPC if unused, restricting REST API access, and keeping all plugins and themes up to date. Check the Security tab for specific findings.
jQuery loaded alongside a modern framework
Both jQuery and React are loaded. Modern frameworks handle DOM manipulation natively. jQuery may be unnecessary and adds ~30KB to the page weight. Check the Performance tab for bundle analysis.
No build tool detected
A framework (Complianz) was detected but no bundler was identified. The build tool may not be detectable from output patterns, or the site may use the framework's built-in bundler.
Complex technology stack detected
28 technologies identified. A complex stack increases maintenance burden and attack surface. Consider whether all components are actively needed.
Show your score
Drop this badge on your README, marketing site, or status page. It auto-updates every time the audit re-runs and links back to this report.
This badge auto-updates with your latest scan result.
[](https://beavercheck.com/sites/ecolecybele.com)<a href="https://beavercheck.com/sites/ecolecybele.com"><img src="https://beavercheck.com/badge?url=https%3A%2F%2Fecolecybele.com" alt="BeaverCheck Score"></a>https://beavercheck.com/badge?url=https%3A%2F%2Fecolecybele.comExport & share
Download the audit, share with your team, or grab a fix plan ready to copy into your tracker.
Copies markdown to clipboard
Fix Plan
Three-week roadmap to ship the audit's findings, with one-click copy targets for your tracker.
Three-week fix plan
2 sprints · 5h total → projected A (90)
Sprint 1: Quick Wins
+6Highest ROI — low effort, high impact
- · HSTS header is missing
- · 1 image-in-link without alt text
- · 1 link(s) with no accessible text
- · 4 button(s) with no accessible text
Sprint 2: Core Fixes
+3Medium effort, high structural impact
- · Content-Security-Policy header is missing